
Security Insights
Deep dives, expert analysis, and practical guidance on exposure management, adversarial validation, and the future of AI-driven exposure management.
Building an AI Harness for Offensive Security: What It Takes to Turn LLMs Into Reliable Pentest and Validation Operators
The model is 20% of the problem. Here is the engineering story behind the orchestration, tooling, middleware, and infrastructure that turns a capable LLM into a reliable penetration testing operator.
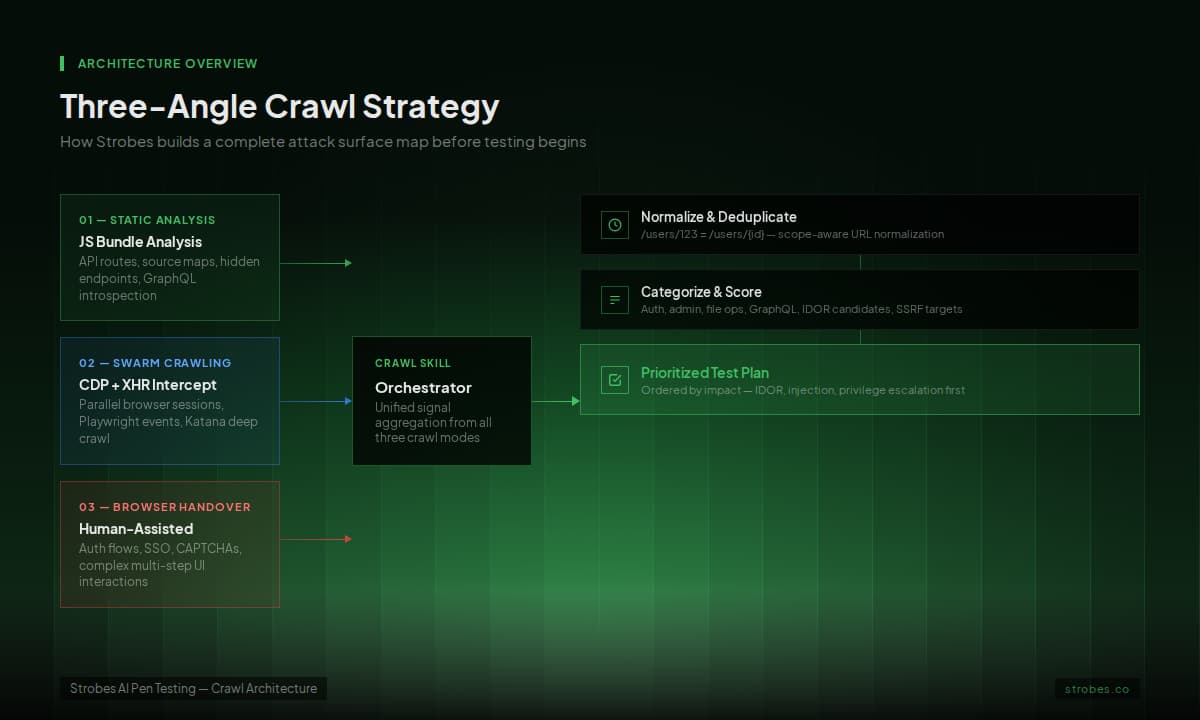
Why Crawling Is the Hardest Part of AI-Powered Pen Testing (And How We Fixed It)
AI agents are brilliant at reading code but terrible at navigating browsers. Here's how Strobes combines static analysis, CDP-based swarm crawling, and human browser handover to build a complete attack surface map before testing begins.
What Is a Red Team Assessment? (And How It Differs From Pentesting)
A red team assessment is a goal-based attack simulation that tests whether your SOC would catch a real adversary. Here is what one looks like end to end, with the detection gaps it exposes.
Wireless Penetration Testing Guide
A weak Wi-Fi key cracked from the parking lot can undo every firewall you own. Here is the wireless penetration testing workflow, with real hcxdumptool and hashcat output and the EAP-TLS fix that ends it.
Internal Network Penetration Testing Guide
Plug in a laptop, run one tool, and you often own the domain by lunch. Internal network penetration testing proves how far a single foothold reaches, and this guide shows the exact commands and output.
Types of Penetration Testing: Which One Does Your Business Need?
Cybersecurity isn’t just about compliance checklists or antivirus software anymore. Businesses are dealing with increasingly advanced threats, and attackers are not bound by boundaries or playbooks. They’ll go after weak credentials, misconfigured servers, exposed APIs, and even unsuspecting employe
Penetration Testing Methodology: Step-by-Step Breakdown for 2025
Cyber threats are sharper and more widespread than ever before, consistently finding new entry points across our intricate digital world, from sprawling cloud environments and complex APIs to the mobile apps we rely on and even dynamic containerized workloads. Relying solely on reactive security mea
How to Tame Your Multi-Cloud Attack Surface with Pentesting
Let’s face it most organizations aren’t using just one cloud provider anymore. Maybe your dev team loves AWS. Your analytics team prefers GCP. And someone else decided Azure was better for access controls. The result? A multi-cloud setup that’s great for flexibility but a nightmare for security and
What is Continuous Penetration Testing? An Ultimate Guide
Continuous penetration testing is a modern security approach that performs real-time or near-real-time simulations of cyberattacks against an organization’s digital assets, ensuring vulnerabilities are identified and addressed as they emerge. Unlike traditional penetration testing, which provides on
What Is Mobile App Penetration Testing? (iOS and Android)
Mobile app penetration testing attacks the iOS or Android client the way an adversary does: decompiling the binary, reading what it writes to disk, and rewriting its logic at runtime. Here is how a real engagement runs.
WordPress Security and Penetration Testing Guide
WordPress runs 40% of the web, and the core almost never lets you in. Plugins do. Here is how to pentest a WordPress site with wpscan and harden what attackers actually hit.
Your Go-To Web Application Pentesting Checklist
Web applications are integral to modern business operations, facilitating customer engagement, financial transactions, and internal processes. However, their widespread use and complexity make them prime targets for cyber threats. A single vulnerability can lead to unauthorized access, data breaches