
Security Insights
Deep dives, expert analysis, and practical guidance on exposure management, adversarial validation, and the future of AI-driven exposure management.
CVE-2025-55182: React2Shell RCE Demands Immediate Security Action
React2Shell exposes a fundamental flaw in how React Server Components interpret untrusted data, turning a routine hydration step into a reliable remote execution pathway. Introduction If you work with React, Next.js, or any framework that leans on React Server Components (RSC), this is the one vulne
Top CVEs of October 2025
October wasn’t short on headlines, but these CVEs did more than make the news. They reshaped how organizations view exposure, privilege, and trust across their environments. Top CVEs of October 2025 spotlights the vulnerabilities that drove real-world exploits, privilege abuse in the cloud, and syst
CVE-2025-61882 Explained: The Oracle Zero-Day Breach That Hit Enterprises Hard
A critical zero-day vulnerability in Oracle E-Business Suite (EBS) was exploited by the Cl0p ransomware group in mid-2025. The flaw, later tracked as CVE-2025-61882, allowed remote code execution without authentication, giving attackers complete control over affected systems. On the Strobes Vulnerab
Top CVEs & Vulnerabilities of September 2025
CVEs & Vulnerabilities of September 2025 reveal a wave of high-impact flaws that security teams cannot afford to ignore. From unauthenticated exploits in FreePBX to privilege escalation in Android and root-level risks in Cisco firewalls, attackers are moving fast to weaponize these weaknesses. This
How Regular CVE Scanning Reduces the Risk of RCE Attacks
Remote Code Execution (RCE) attacks remain one of the most dangerous cybersecurity threats, allowing attackers to take full control of systems and cause severe business damage. Regular CVE scanning is a key part of how to prevent RCE attacks, helping organizations identify unpatched vulnerabilities,
Active Directory Penetration Testing Checklist
Most domains fall without a single CVE. This Active Directory penetration testing checklist walks the phases with real Kerberoast and Certipy output, a findings table, and the controls that actually break each path.
Top CVEs & Vulnerabilities of August 2025- Risks, Impacts & Fixes
August 2025 saw critical CVEs surface, including high-impact flaws in WinRAR and Microsoft SharePoint. This blog highlights the most urgent vulnerabilities, their potential business risks, and the patch actions security teams should prioritize to stay ahead of threats.
Top CVEs of July 2025: Exploits, Exposure, and the Risks
Some CVEs quietly fade into vendor advisories. Others don’t wait. The Top CVEs of July gained traction quickly - through public exploits, active scanning, or visibility in high-usage systems. This list isn’t built on CVSS alone. The Top CVEs of July were selected based on exploit availability, attac
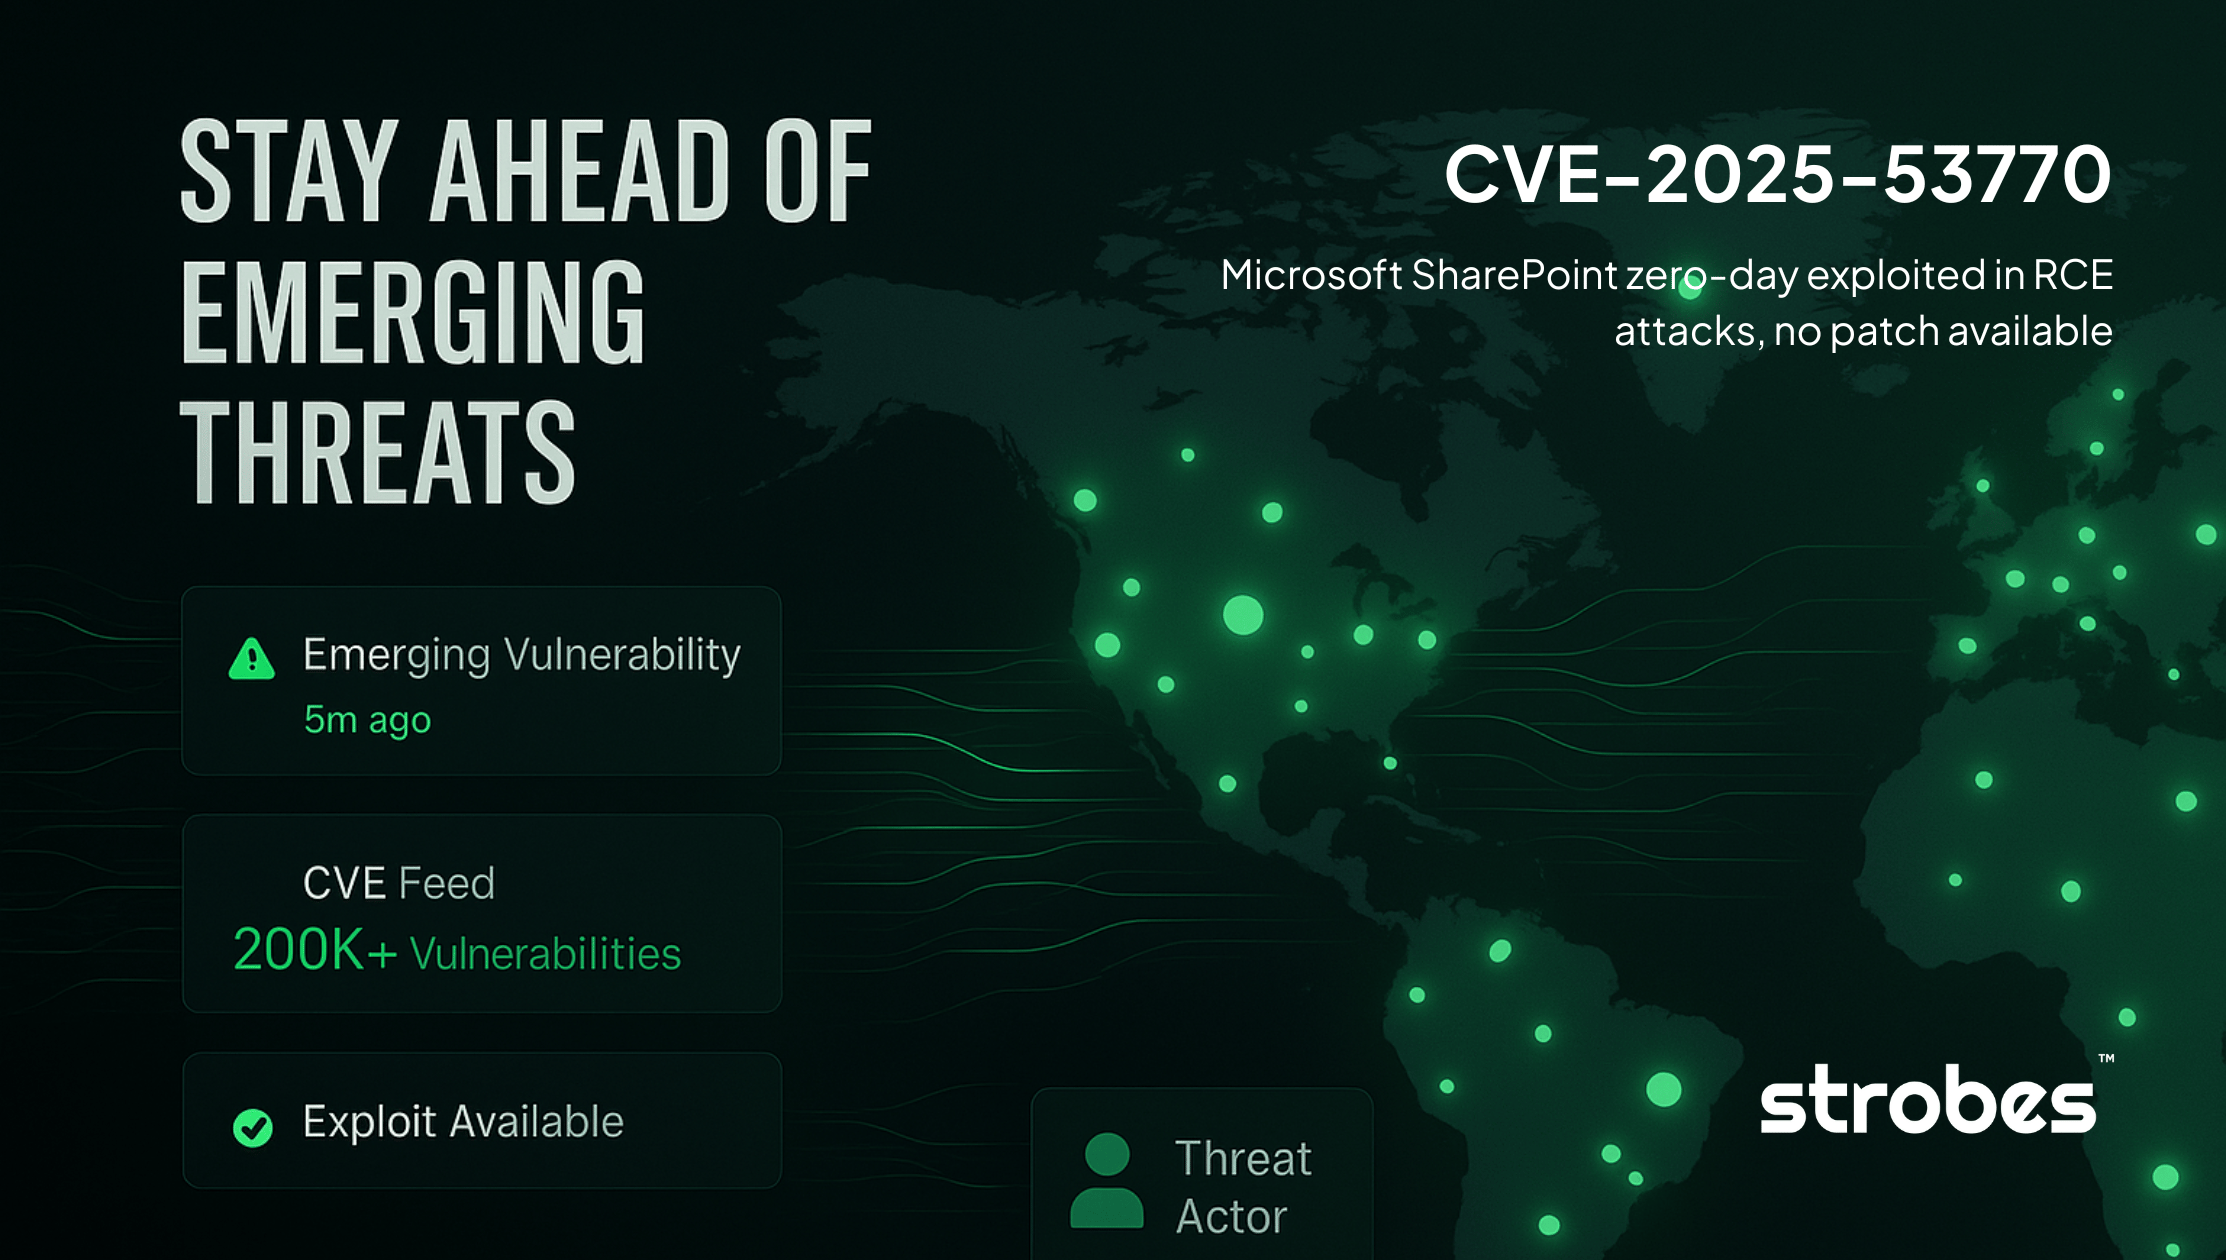
CVE-2025-53770 - Microsoft SharePoint zero-day exploited in RCE attacks
CVE-2025-53770 is a critical remote code execution vulnerability (CVSS 9.8) in on-premises Microsoft SharePoint Server that allows unauthenticated attackers to completely compromise servers through deserialization of untrusted data. The Microsoft SharePoint Zero-Day vulnerability is currently being
Top 5 High-Risk CVEs of June 2025
Each month brings a flood of vulnerability disclosures. But only a few truly matter. The ones being exploited. The ones buried in critical systems. The ones that could take down your environment. In this post, we’ve pulled together the top CVEs of June 2025 not based on volume, but based on risk. Re
Top CVEs of May 2025: Critical Exploits, Real-World Attacks, and What You Must Patch Now
Each month brings new vulnerabilities, and some aren’t just bugs, they’re invitations. The CVEs of May 2025 made headlines not just for their technical depth, but for how quickly they were exploited. From remote code execution flaws in widely used enterprise platforms to privilege escalation bugs in
Why Fixing Every Vulnerability Is Wasting Time and Your Team’s Budget
We have discovered 10,000 vulnerabilities this year. Great, now what? This sounds like a lot of work has been done, but in reality, it is just noise, not a signal. After every scan, you get a massive list of CVEs, misconfigurations, and alerts but without prioritization and targeted vulnerability fi