
Security Insights
Deep dives, expert analysis, and practical guidance on exposure management, adversarial validation, and the future of AI-driven exposure management.
NIST just published AI prompts for CSF 2.0. Here is what to settle first
NIST's draft SP 1353 provides AI prompts for three CSF 2.0 tasks and says weeks of drafting compresses into hours. Here is what the prompts can draft, what only humans can validate, and the four things to settle before anyone opens a model.
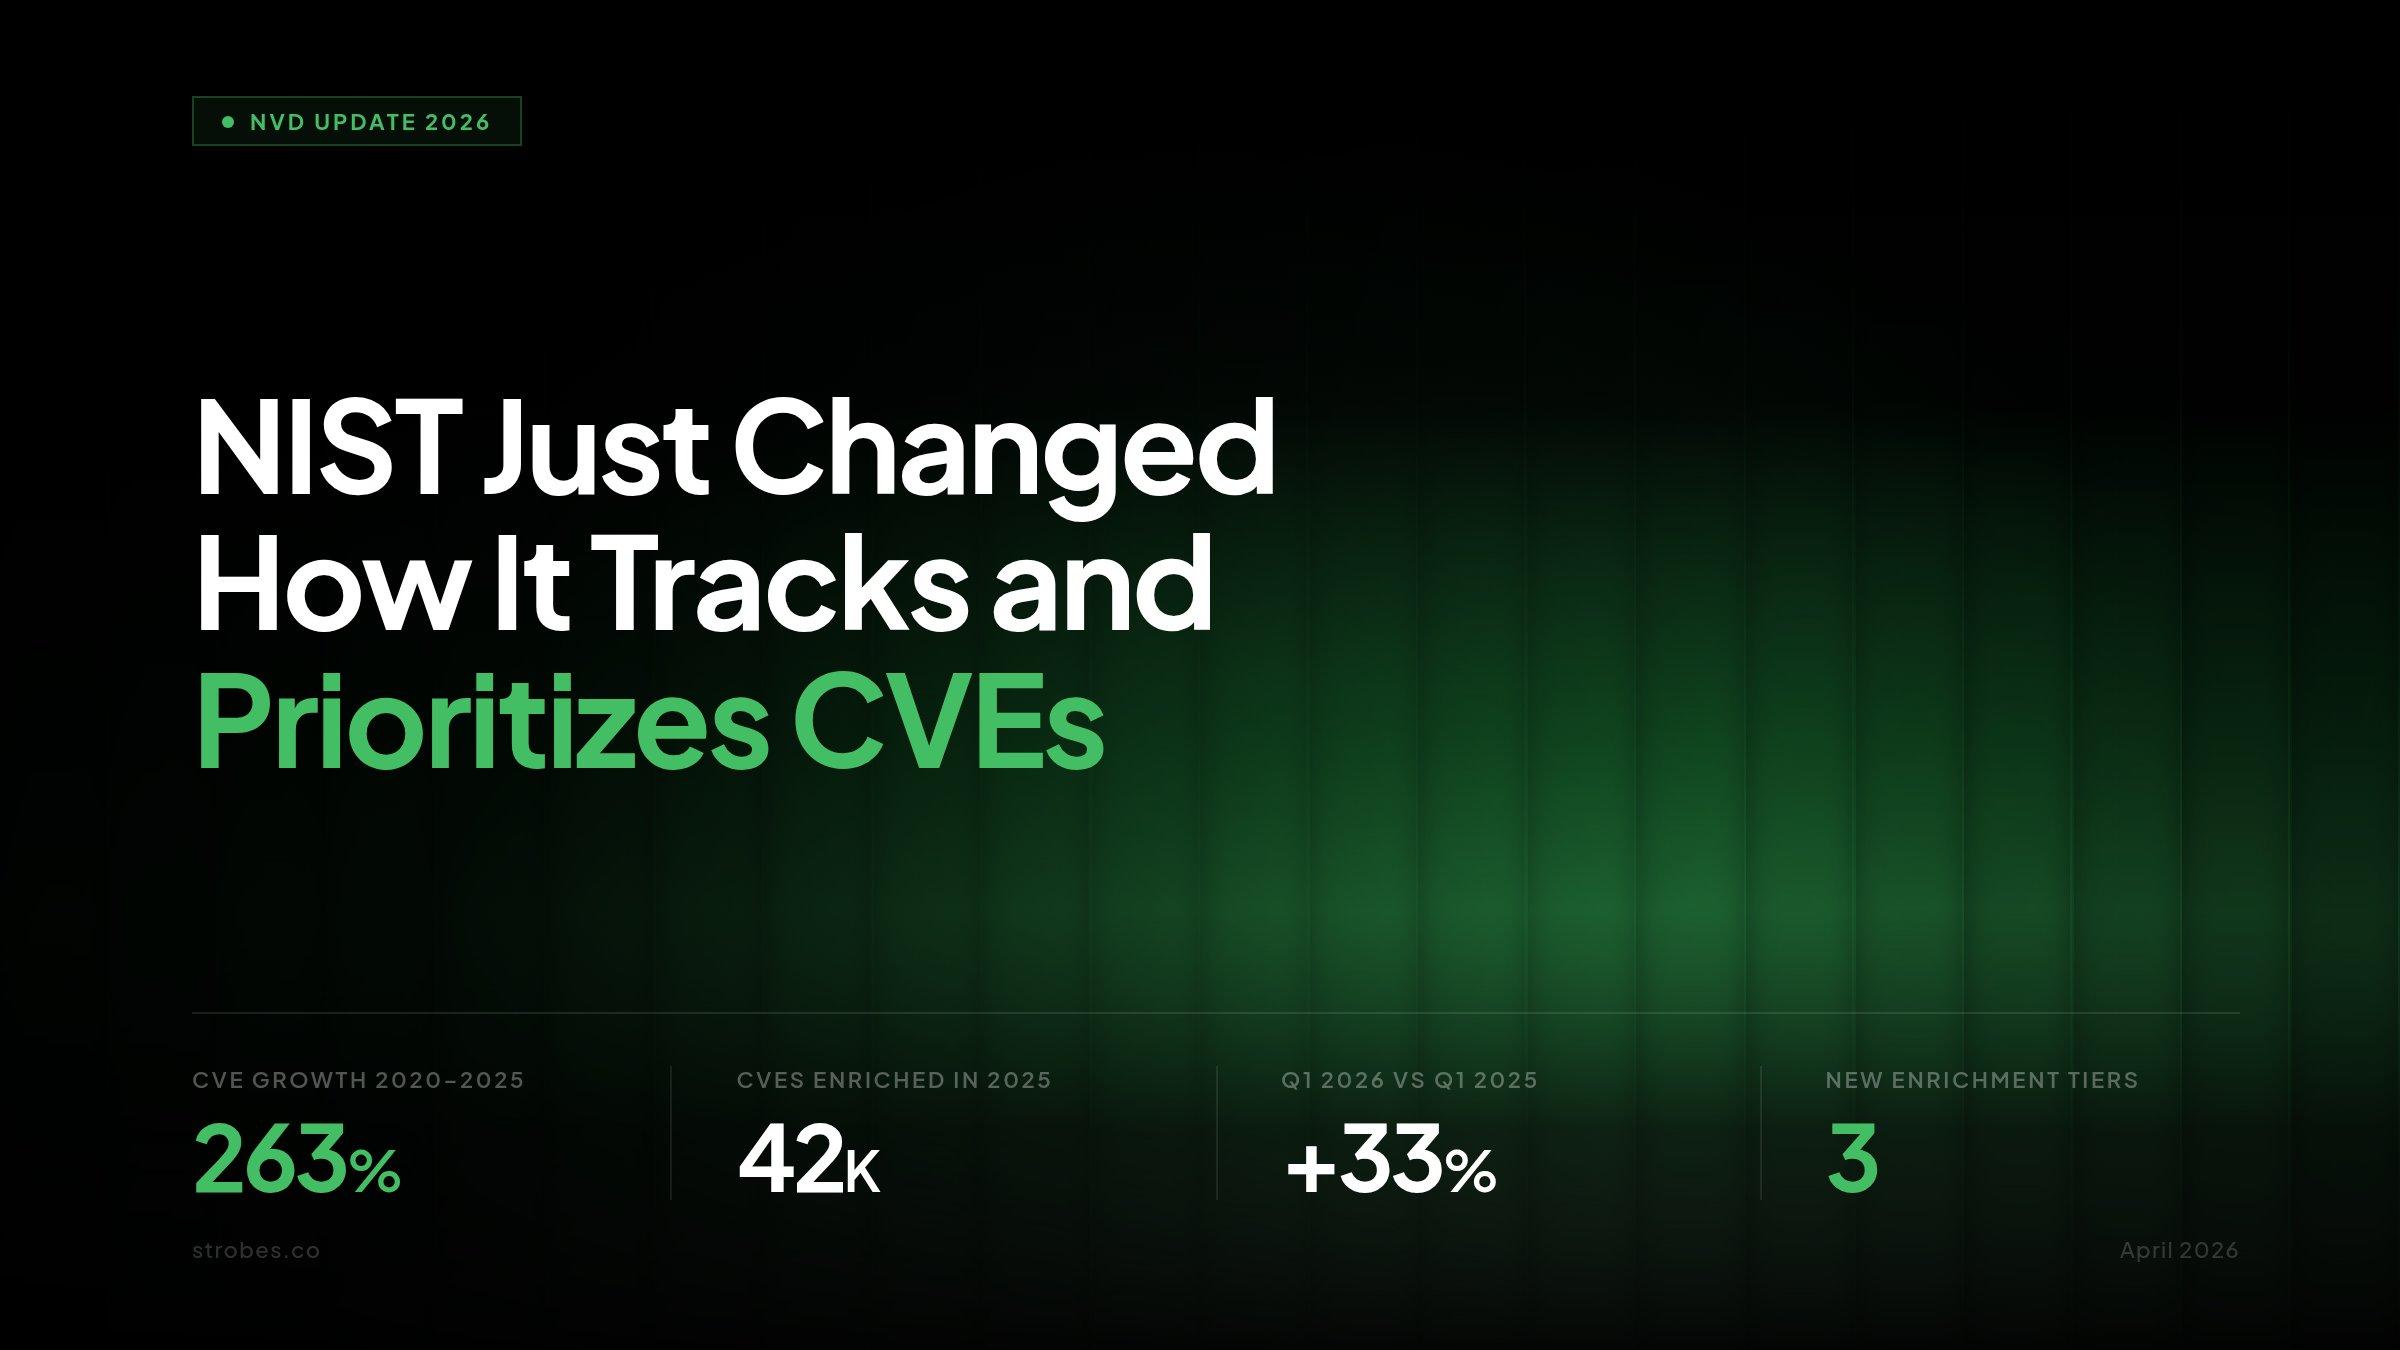
NIST Just Changed How It Tracks and Prioritizes CVEs
NIST has changed how it enriches CVEs in the NVD. Learn what the new risk-based triage model means for your vulnerability management program, scanner data, and remediation workflows.
Ransomware Readiness Assessment- A Strobes Guide to Resilience, ROI and Compliance
Ransomware can halt operations, drain budgets, and erode trust. A ransomware readiness assessment helps CISOs validate backup recovery, control high-risk access, and prove resilience against evolving threats. By aligning with CISA and NIST guidance, organizations gain clear steps, measurable outcome
Penetration Testing Standards: PTES, OSSTMM, NIST, and OWASP
PTES, OSSTMM, NIST SP 800-115, and the OWASP guides are the four standards behind professional pentesting. Here is what each covers, how they stack, and how to spot a vendor faking it.