
Security Insights
Deep dives, expert analysis, and practical guidance on exposure management, adversarial validation, and the future of AI-driven exposure management.
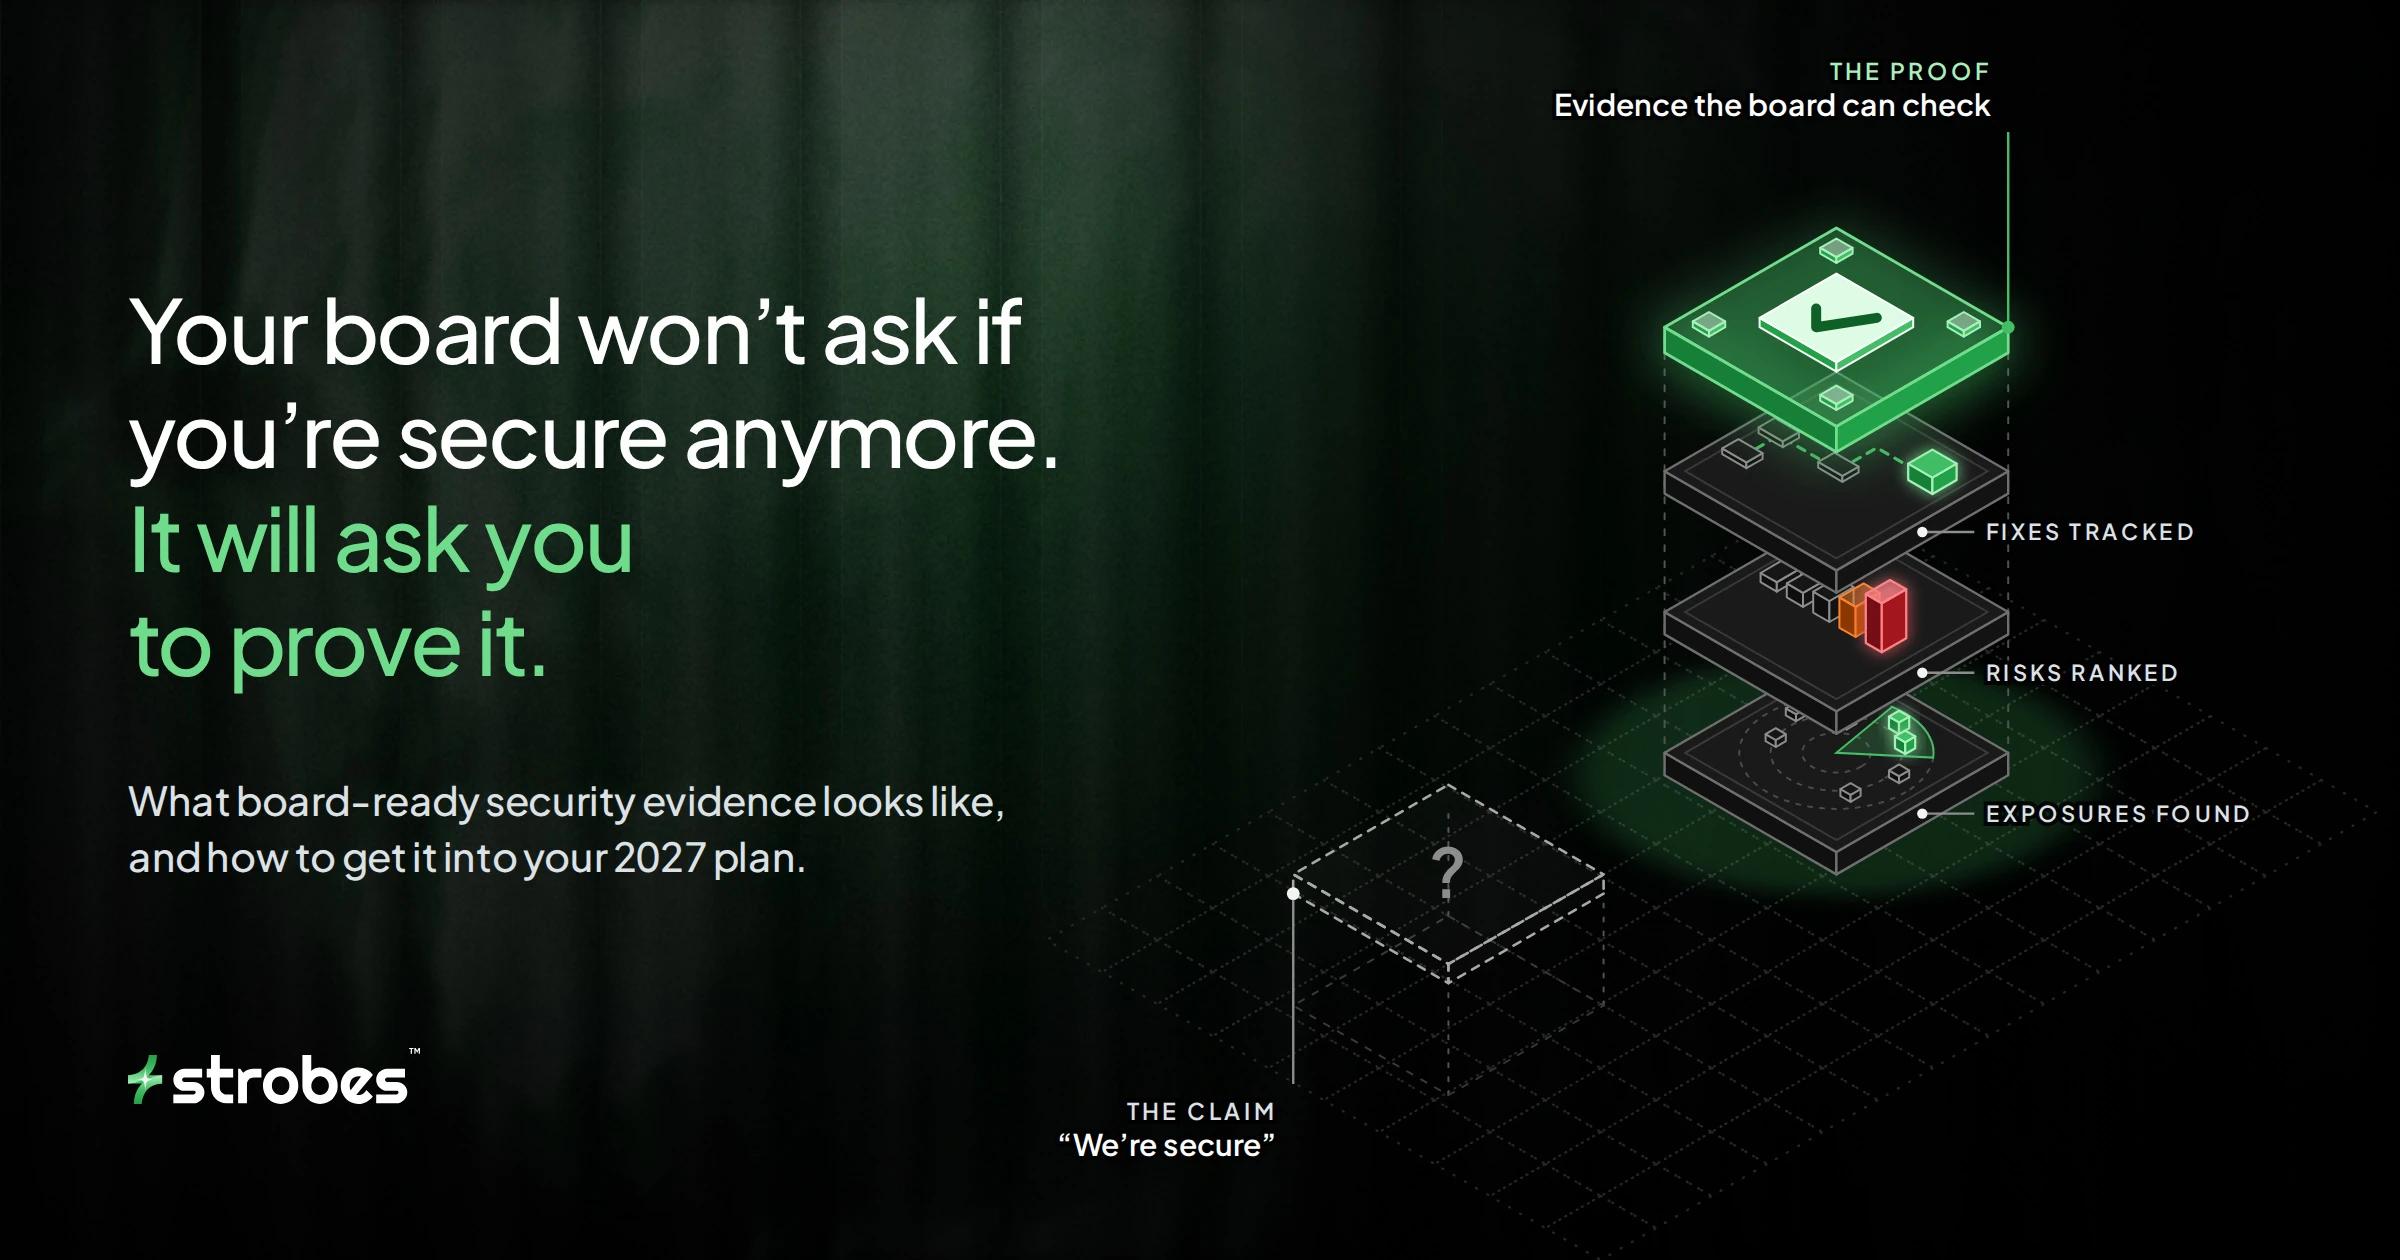
Your board won't ask if you're secure anymore. It will ask you to prove it.
Boards now ask for evidence that cyber risk is within appetite. What board-ready security evidence looks like, how to govern autonomous testing, and how to get it into your 2027 plan.
Top CVEs of August 2026
August's CVSS 7.0 was a Lazarus zero-day exploited for five weeks. Its CVSS 10.0 needed no patch at all. The top CVEs of August 2026, ranked by exploitation evidence rather than severity, with remediation steps for all five.
How Strobes AI identifies and exploits a SQL injection vulnerability
See how Strobes AI runs autonomous SQL injection testing, finding an injectable parameter, proving exploitability, and shipping evidence for remediation.
What Counts as Valid Proof in an Agentic Pentest?
Valid proof in an agentic pentest is reproducible, in-scope, and attributable evidence of exploitability. What counts, what doesn't, and how to prove it.
ISO 27001 Penetration Testing Requirements
ISO 27001:2022 never names penetration testing, yet it is how you evidence Annex A 8.8 and 8.29 at a surveillance audit. The honest read on required vs expected, with the 2013 lineage and the Oct 2025 deadline.
SOC 2 Penetration Testing Requirements
SOC 2 never names penetration testing in any criterion, yet auditors treat it as the load-bearing evidence for CC4.1 and CC7.x. Here is the gap between the letter and the audit.