
Security Insights
Deep dives, expert analysis, and practical guidance on exposure management, adversarial validation, and the future of AI-driven exposure management.
Vulnerability Validation: Why Most of Your Scanner Backlog Is Noise
Vulnerability validation proves which scanner findings are real, reachable, and exploitable. Why manual triage fails and how agentic validation scales.
How to Pentest Single-Page Applications (React, Angular, Vue)
Learn how to pentest React, Angular, and Vue SPAs. Covers DOM XSS, client-side routing bypass, JS bundle secrets, and why traditional DAST scanners fail.
Bug Bounty vs. Pentesting vs. AI Pentesting: Which Model Fits Your AppSec Program?
Bug bounty vs pentesting vs AI pentesting: compare costs, coverage, compliance, and when to use each model. Build a layered AppSec testing strategy.
DAST vs. Pentesting vs. AI Pentesting: What Each One Actually Finds
Compare DAST, manual pentesting, and AI pentesting. Learn what each approach finds, misses, costs, and when to use each for full application security coverage.
Continuous Application Pentesting for DevSecOps Teams
How DevSecOps teams integrate continuous application pentesting into CI/CD pipelines. AI-driven testing, run-over-run diffing, and developer workflow integration.
Pentesting Microservices Architecture: Why Traditional Methods Fall Short
Why traditional pentesting misses 90% of microservices attack surface. Learn how to test East-West traffic, service mesh, and Kubernetes security at scale.
Application Pentesting for SaaS Companies: Meeting SOC 2 and ISO 27001
How SaaS companies should structure application pentesting for SOC 2 and ISO 27001 compliance. AI-driven continuous testing vs annual manual engagements.
How to Catch the Blind Bugs Scanners Miss
Out-of-band validation detects blind SSRF, blind SQLi, and out-of-band XXE that return no in-band response. Learn how it works and why it matters.
5 Vulnerabilities in Every Vibe-Coded App
The 5 security flaws AI coding assistants ship by default: missing authz, leaked secrets, weak JWTs, IDOR, eval RCE — with detection queries and fixes for each.
Threat Modeling Explained: STRIDE and Methodology
Threat modeling finds design flaws on a whiteboard, before code exists. A worked STRIDE pass on a login system, attack trees, and why DREAD lost favor.
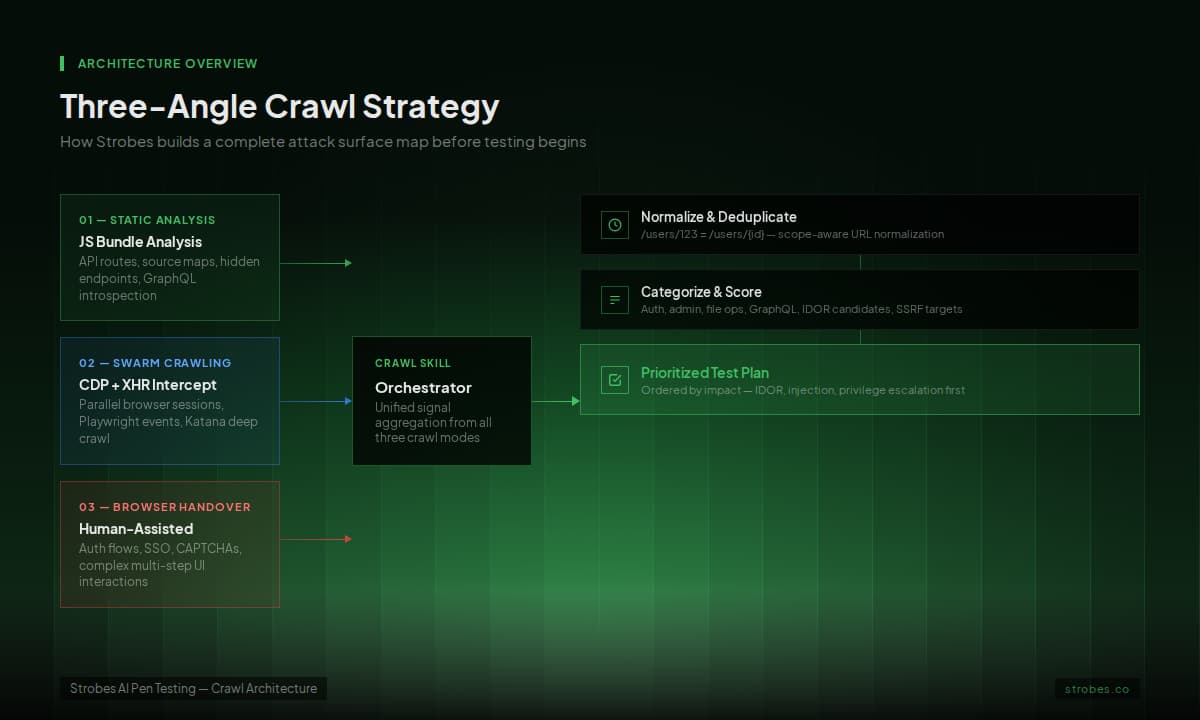
Why Crawling Is the Hardest Part of AI-Powered Pen Testing (And How We Fixed It)
AI agents are brilliant at reading code but terrible at navigating browsers. Here's how Strobes combines static analysis, CDP-based swarm crawling, and human browser handover to build a complete attack surface map before testing begins.
Secure Code Review: A Complete Guide
A senior reviewer's guide to secure code review: trace taint from source to sink, write real Semgrep and CodeQL rules, and gate findings at PR time.