
Security Insights
Deep dives, expert analysis, and practical guidance on exposure management, adversarial validation, and the future of AI-driven exposure management.
Introducing Red Loop: continuous, proven testing of your whole attack surface
Red Loop brings continuous offensive testing to Strobes Attack Surface Management. It discovers what you own, scans it the same way every time, and sends results to AI agents that attack and validate them. Only proven findings reach your queue.
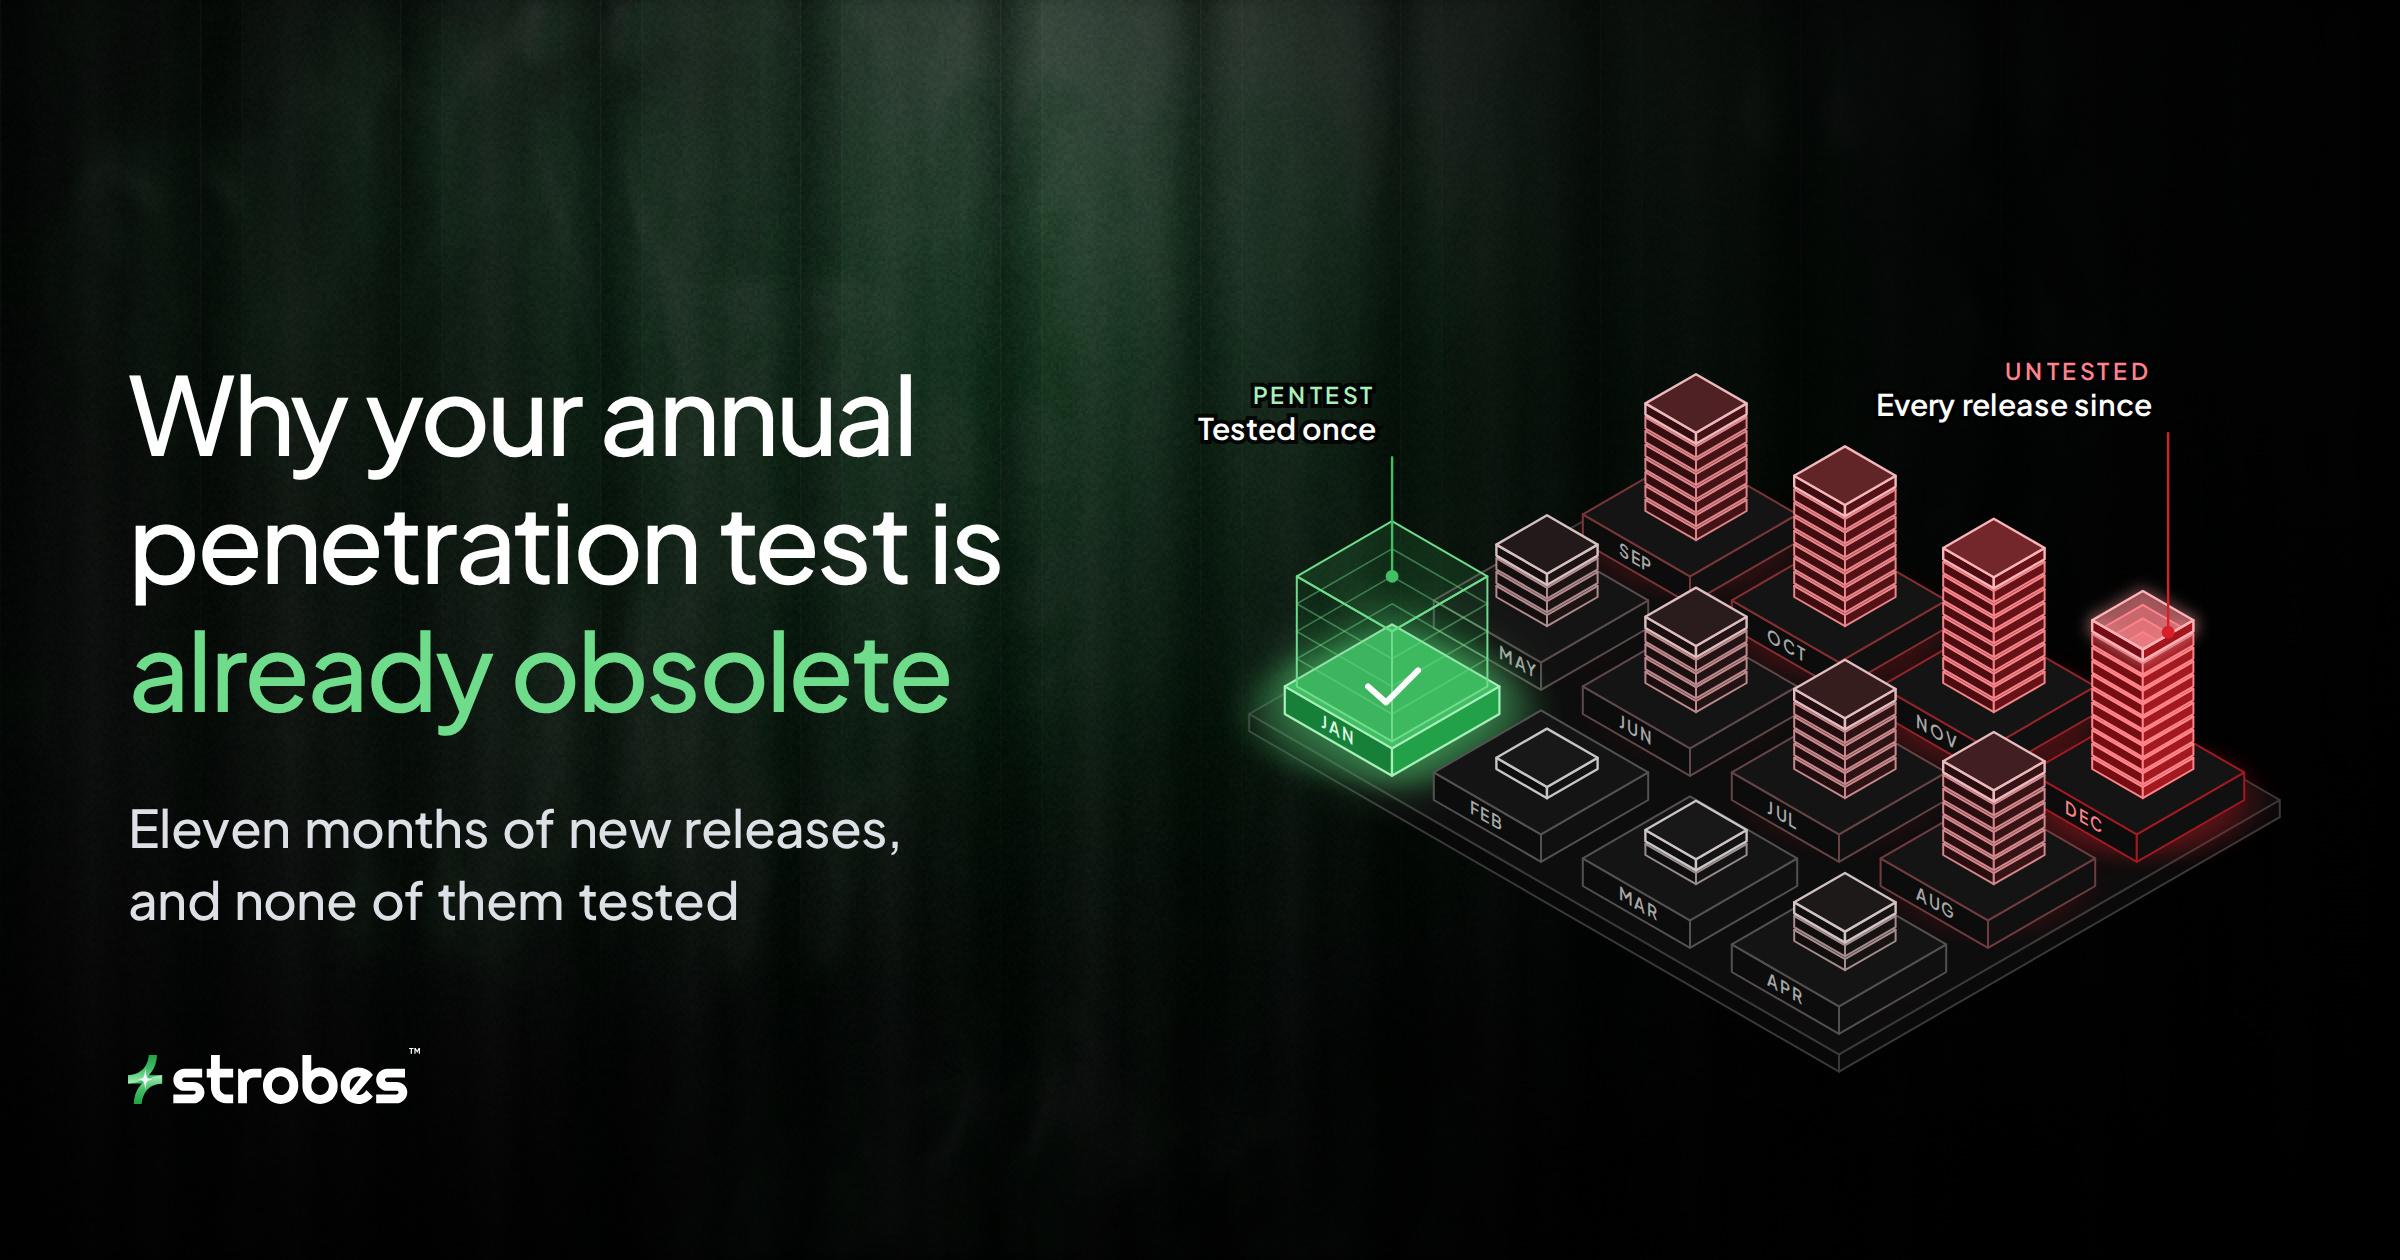
Why your annual penetration test is already obsolete
Your annual pentest describes an environment that no longer exists. Here is how continuous offensive security testing closes the gap, and what it takes to run one.
Strobes joins OpenAI's Daybreak program
OpenAI gates its cyber models behind an application, identity checks, and workspace scoping. Strobes is now verified for Daybreak.
Build vs Buy Agentic Pentesting and What the DIY Path Costs
Everyone can build a working pentest agent in a weekend. Owning it for two years is the hard part: the four costs nobody adds up, and the seven requirements a demo never has to meet.
How to Achieve Cheaper, Faster and Accurate Pentests
Cheaper, faster and accurate pentests were never a real tradeoff. Context removes it: one graph of assets, code and cloud that every engagement reads from and writes back to.
How to run an agentic pentesting POC
A 10-day testing playbook to evaluate agentic pentesting vendors: what to test each day, the red flags to watch for, and a scorecard that works with any vendor.
Tooling as Code and Structured Scratchpads
The two changes that moved our AI security agents furthest this year had nothing to do with the model. Here is how tooling as code and structured scratchpads reshaped how the agents act, and how they prove a finding is real.
What to Evaluate Before You Let an AI Agent Exploit Your Systems
An AI agent that can exploit your systems does an attacker's work. Here are the seven governance checks to clear before you authorize agentic pentesting in production.
Human-in-the-loop security: why AI findings need human validation
An AI pentester can hand you a critical finding in minutes. The only question that matters is whether you believe it. Here is why human validation turns a claim into proof.
Strobes Agentic Pentesting: A pen-tester experience and point of view
Eleven validated Critical and High findings from Strobes AI's autonomous pentesting agents, each with the agent's reasoning, the request sent, and the response that proved it.
10 Best Open Source Agentic Pentesting Tools in 2026
Compare the 10 best open source agentic pentesting tools for self-hosted workflows, from PentAGI and PentestGPT to CAI, Strix, and VulnBot.
Vulnerability Chaining: How Agentic Pentesting Proves Attack Paths
Three low-severity findings can chain into one critical breach. See why CVSS misses chained risk and how agentic pentesting proves or rejects each attack path.