
Security Insights
Deep dives, expert analysis, and practical guidance on exposure management, adversarial validation, and the future of AI-driven exposure management.
How Agentic Pentesting Separates Test Failures From Real Security Findings
Agentic pentesting reliability on unstable apps: a six-state failure taxonomy, safe retry rules, and what a trustworthy pentest report must disclose.
What Counts as Valid Proof in an Agentic Pentest?
Valid proof in an agentic pentest is reproducible, in-scope, and attributable evidence of exploitability. What counts, what doesn't, and how to prove it.
Bug Bounty vs. Pentesting vs. AI Pentesting: Which Model Fits Your AppSec Program?
Bug bounty vs pentesting vs AI pentesting: compare costs, coverage, compliance, and when to use each model. Build a layered AppSec testing strategy.
Pentesting In-House vs. Outsourcing: Cost, Coverage, and the Third Option
Compare in-house vs outsourced pentesting on cost, coverage, and depth. Discover why AI pentesting is the third option that changes the math for security teams.
How to Catch the Blind Bugs Scanners Miss
Out-of-band validation detects blind SSRF, blind SQLi, and out-of-band XXE that return no in-band response. Learn how it works and why it matters.
5 Vulnerabilities in Every Vibe-Coded App
The 5 security flaws AI coding assistants ship by default: missing authz, leaked secrets, weak JWTs, IDOR, eval RCE — with detection queries and fixes for each.
Black-Box Agentic Scanners: Strengths and Their Ceiling
Black box agentic pentesting finds real CVEs fast and proves them, but where does it hit a ceiling? An honest, category-level verdict.
Why AI-Generated Exploit Code Must Run in Isolation
Agent-written exploit code is the new RCE vector aimed at the tester. Here's why per-task isolation and egress control are non-negotiable.
What Is Agentic Pentesting? The Complete Guide for Security Teams (2026)
Agentic pentesting uses specialized AI agents to test your entire attack surface in hours, not weeks. Here is how it works, what surfaces it covers, how safety is enforced, and how to evaluate platforms with real benchmarks.
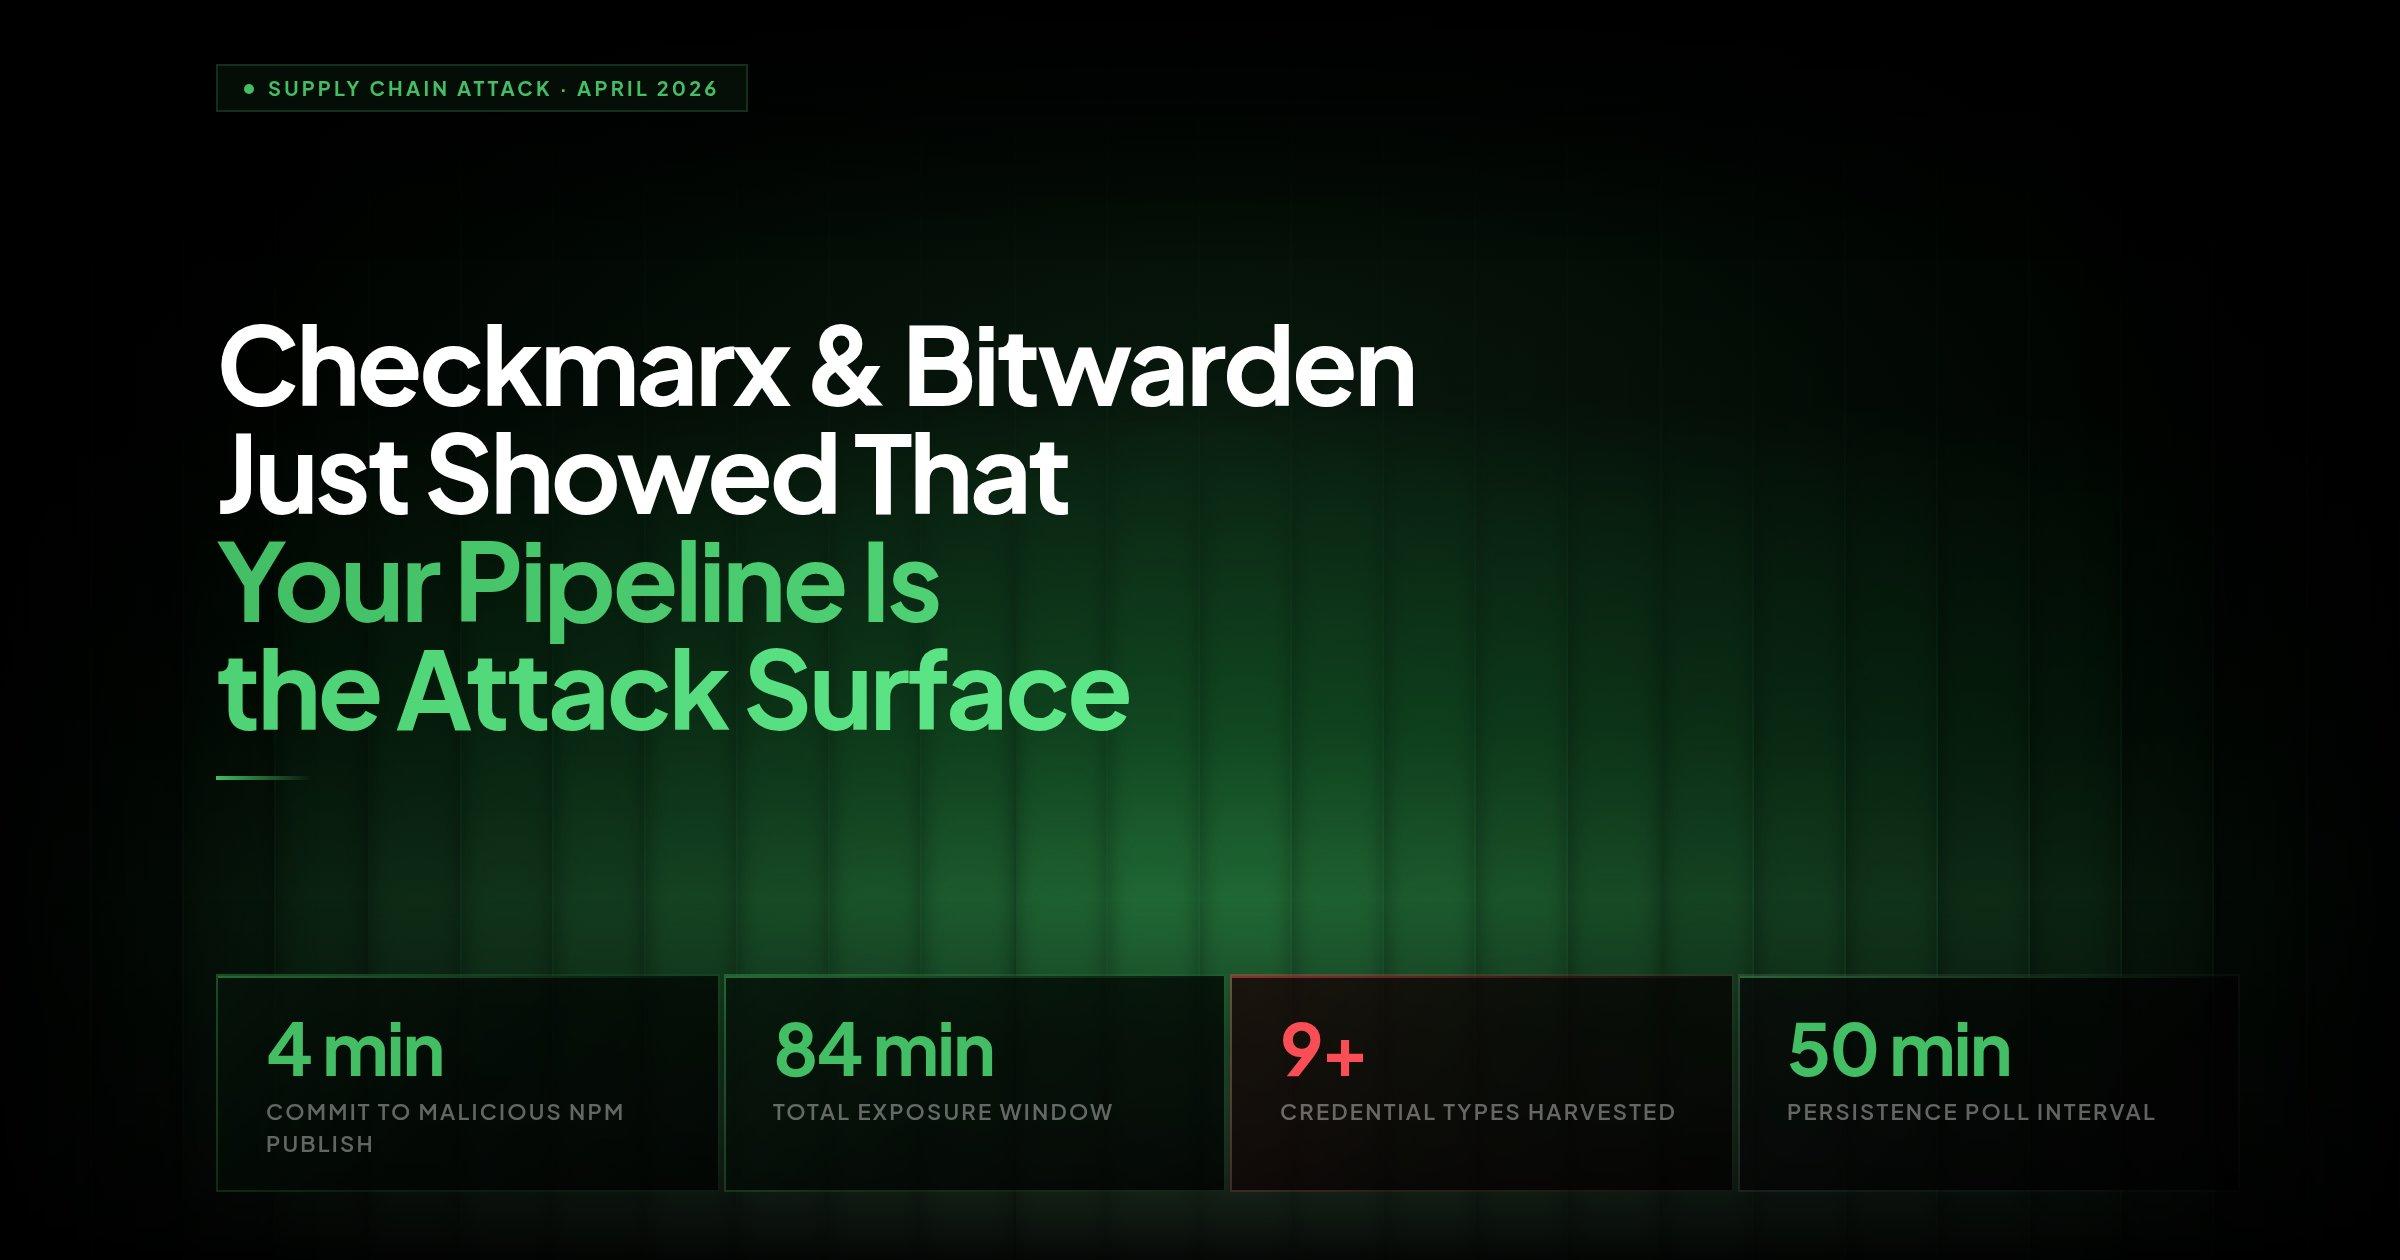
Checkmarx and Bitwarden Just Showed That Your Pipeline Is the Attack Surface
How the Checkmarx supply chain attack compromised Bitwarden's CLI pipeline in four minutes, what was stolen, and the program design gap that made it possible.
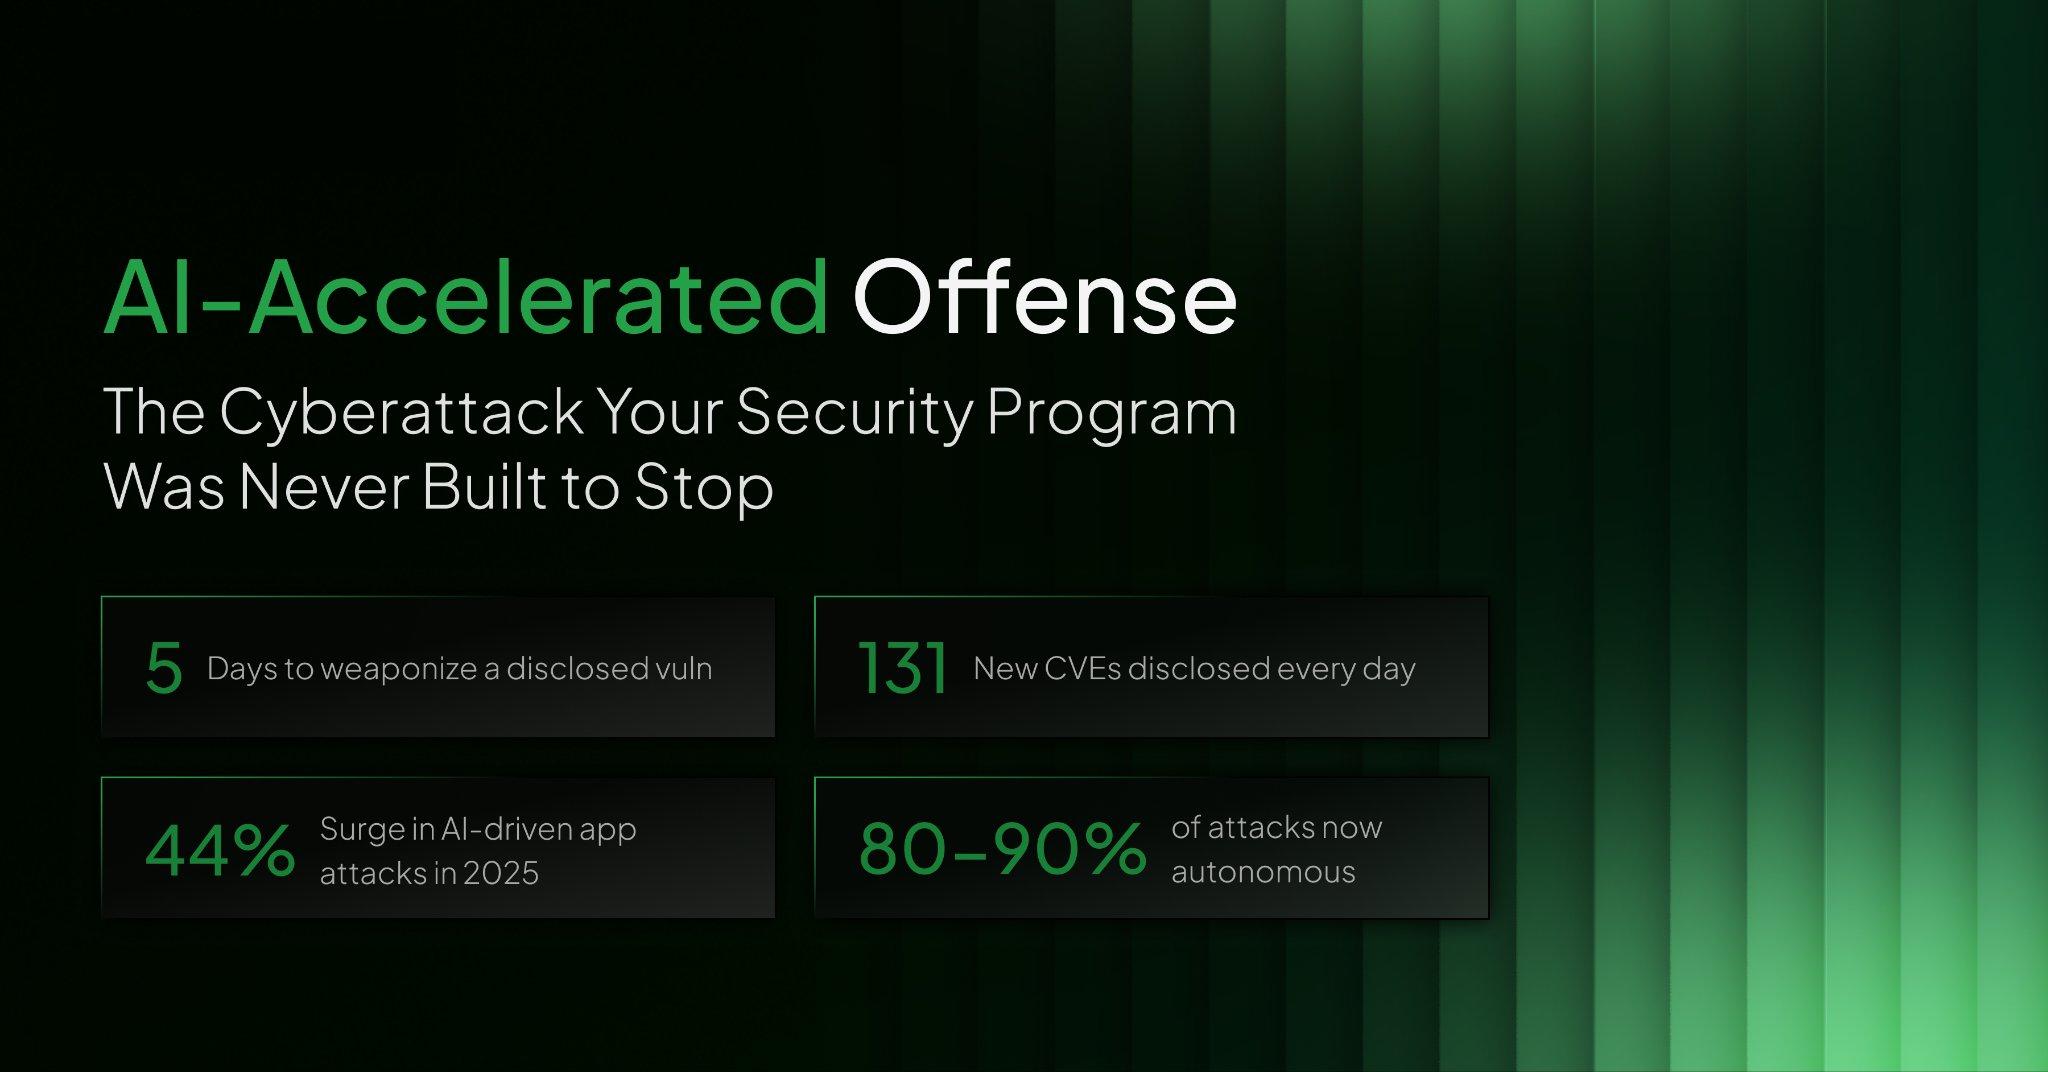
AI-Accelerated Offense: The Cyberattack Your Security Program Was Never Built to Stop
AI-Accelerated Offense uses autonomous agents to run the full cyberattack chain in hours. A frontier AI model found thousands of zero-day vulnerabilities across every major OS and browser in weeks. See how it works, why your security program is already behind, and what to do now.
Best AI Pentesting Tools in 2026: Ranked, Priced & Compared (12 Tools)
Which AI pentesting tool actually reduces risk in 2026? We reviewed 12 platforms on autonomy, proof quality, pricing, and what happens after a vulnerability is found.