
Security Insights
Deep dives, expert analysis, and practical guidance on exposure management, adversarial validation, and the future of AI-driven exposure management.
Is Claude Mythos the End of Pentesting?
Claude Mythos found thousands of zero-days in Linux, browsers, and Apache. Does that make pentesting platforms obsolete? Understanding why models, harnesses, and platforms are three different things -- and why smarter AI makes Strobes more valuable, not less.
How to Write an Effective AI Agent Skill: The Four-Layer Architecture
Most teams building AI agents get the ratio wrong: 90% code, 10% methodology. Here is the four-layer architecture Strobes uses to build skills that run complete security assessments autonomously.
Strobes AI: The Agent Stack Specialized for Offensive Security
A deep-dive into the multi-agent architecture behind Strobes AI — 12 purpose-built offensive security agents, the Skills system, Human in the Loop governance, and the architectural properties that make continuous exposure management viable at scale.
Agentic Pentesting with Strobes AI
What happens when you point Strobes AI at a real web app and let it run a full OWASP WSTG assessment with zero hand-holding? 32 tasks, 21 phases, 42 confirmed vulnerabilities — all autonomous.
Building an AI Harness for Offensive Security: What It Takes to Turn LLMs Into Reliable Pentest and Validation Operators
The model is 20% of the problem. Here is the engineering story behind the orchestration, tooling, middleware, and infrastructure that turns a capable LLM into a reliable penetration testing operator.
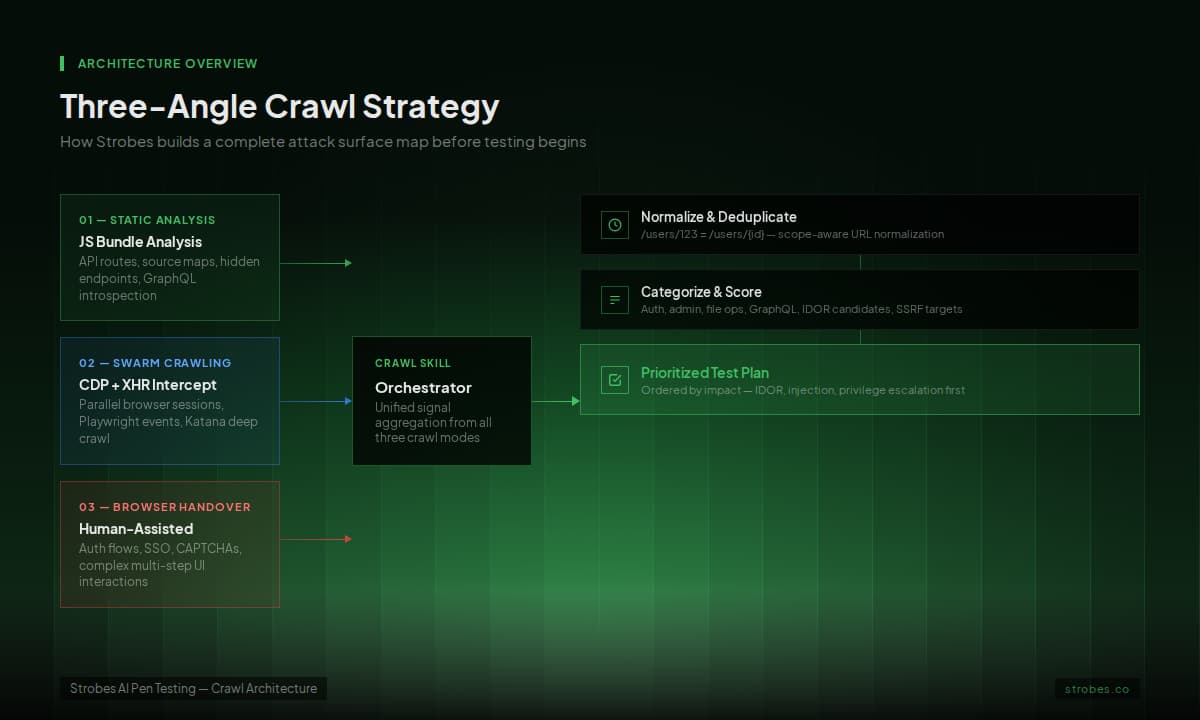
Why Crawling Is the Hardest Part of AI-Powered Pen Testing (And How We Fixed It)
AI agents are brilliant at reading code but terrible at navigating browsers. Here's how Strobes combines static analysis, CDP-based swarm crawling, and human browser handover to build a complete attack surface map before testing begins.
Assumed Breach Assessment Explained
An assumed breach assessment starts with the attacker already inside, so the whole budget goes to detection, response, and blast radius instead of the front door. Here is how it works and when to use it.
The Five Stages of Red Team Methodology
Red team methodology runs in five stages, recon, initial access, foothold and C2, lateral movement and privilege escalation, then actions on objective. Here is each stage with the ATT&CK techniques and the detections that should fire.
Red Team vs Blue Team: A CISO's Guide to Offensive Security
Red team vs blue team is the wrong question for a CISO. The right one is how fast the gap between what red gets away with and what blue catches is closing. Here is how to run both.
What Is a Red Team Assessment? (And How It Differs From Pentesting)
A red team assessment is a goal-based attack simulation that tests whether your SOC would catch a real adversary. Here is what one looks like end to end, with the detection gaps it exposes.
Social Engineering Penetration Testing Guide
A social engineering penetration testing field guide: building an OSINT pretext, running an authorized GoPhish campaign, mapping to MITRE ATT&CK T1566, and the metrics that prove resilience.
IoT Penetration Testing Guide
An IoT penetration testing field guide: binwalk firmware extraction, cracking /etc/shadow with hashcat, dropping to a U-Boot root shell, flashrom SPI dumps, and open MQTT brokers.