
Security Insights
Deep dives, expert analysis, and practical guidance on exposure management, adversarial validation, and the future of AI-driven exposure management.
Building an AI Harness for Offensive Security: What It Takes to Turn LLMs Into Reliable Pentest and Validation Operators
The model is 20% of the problem. Here is the engineering story behind the orchestration, tooling, middleware, and infrastructure that turns a capable LLM into a reliable penetration testing operator.
Threat Modeling Explained: STRIDE and Methodology
Threat modeling finds design flaws on a whiteboard, before code exists. A worked STRIDE pass on a login system, attack trees, and why DREAD lost favor.
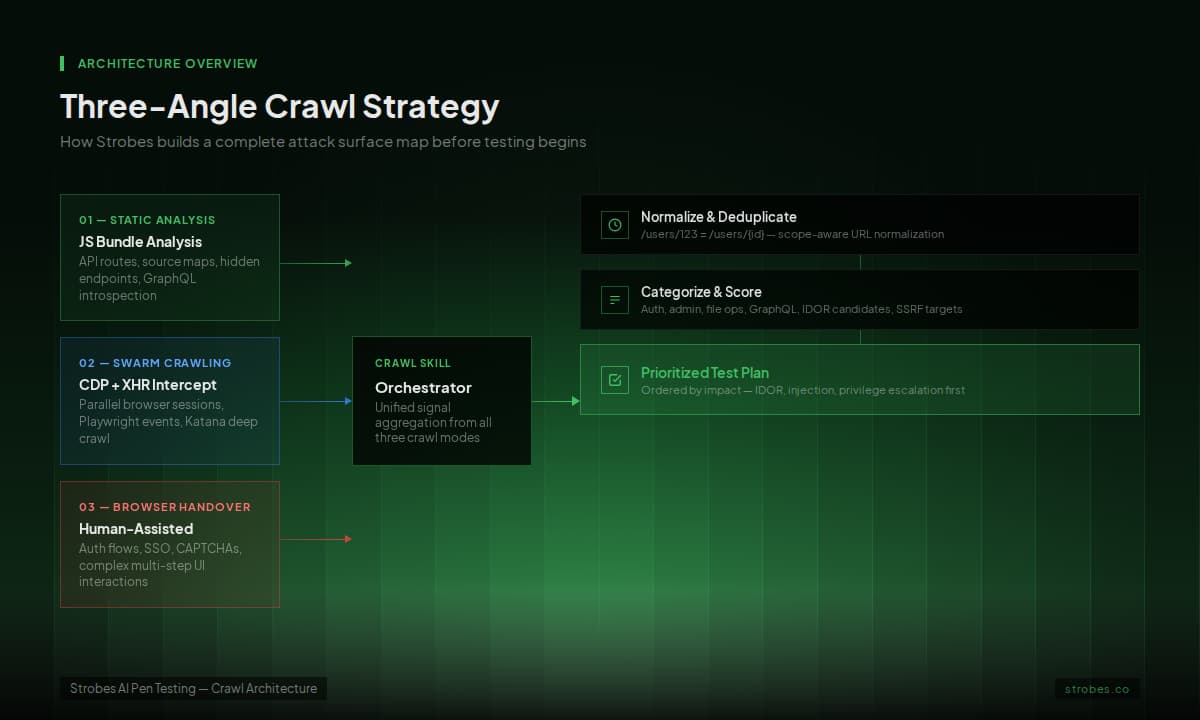
Why Crawling Is the Hardest Part of AI-Powered Pen Testing (And How We Fixed It)
AI agents are brilliant at reading code but terrible at navigating browsers. Here's how Strobes combines static analysis, CDP-based swarm crawling, and human browser handover to build a complete attack surface map before testing begins.
Secure Code Review: A Complete Guide
A senior reviewer's guide to secure code review: trace taint from source to sink, write real Semgrep and CodeQL rules, and gate findings at PR time.
Top Data Breaches of February 2026
February 2026 brought a series of significant data breaches spanning automotive, aviation, hospitality, finance, telecom, and media. The incidents were not driven by a single attack method. Some resulted from credential stuffing, others from ransomware and extortion tactics, and several from inadequ
Assumed Breach Assessment Explained
An assumed breach assessment starts with the attacker already inside, so the whole budget goes to detection, response, and blast radius instead of the front door. Here is how it works and when to use it.
42,900 OpenClaw Exposed Control Panels and Why You Should Care
Over the past two weeks, most coverage around Moltbot and OpenClaw has chased the flashy angle. One-click exploits, remote code execution, APT chatter, scary screenshots. Meanwhile, security teams are doing what they always do when a new tool gets hit. Patch, block ports, rotate keys. That's necessa
Driving CTEM Adoption Across the Enterprise
Most enterprises are not short on security activity. They run scanners, onboard new tools, commission assessments, run internal reviews, and publish regular risk reports. Yet exposure still slips through. Incidents still trace back to issues that were already known. Teams still debate what matters m
The Five Stages of Red Team Methodology
Red team methodology runs in five stages, recon, initial access, foothold and C2, lateral movement and privilege escalation, then actions on objective. Here is each stage with the ATT&CK techniques and the detections that should fire.
Exposure Assessment vs Adversarial Exposure Validation
Your security team just delivered another quarterly report. 847 vulnerabilities discovered. 23 rated critical. 156 high severity. CVSS scores assigned. Remediation priorities set. And yet, like last quarter, the backlog grows faster than your team can patch. Worse, you're left wondering: are we fixi
Adversarial Exposure Validation for Modern Environments
What is Adversarial Exposure Validation? Adversarial Exposure Validation is a structured approach that applies attacker-style actions to confirm how your environment behaves under real pressure. Instead of stopping at detection, it recreates the tactics hostile actors use to prove which exposures ac
Why Deduplication Is the Most Underrated Security Control
Security teams face constant pressure from an overload of alerts and findings. Every new scanner or assessment adds to the pile, making it hard to focus on what matters. Instead of streamlining efforts, these tools often create more confusion by repeating the same issues across reports. This is wher