
Security Insights
Deep dives, expert analysis, and practical guidance on exposure management, adversarial validation, and the future of AI-driven exposure management.
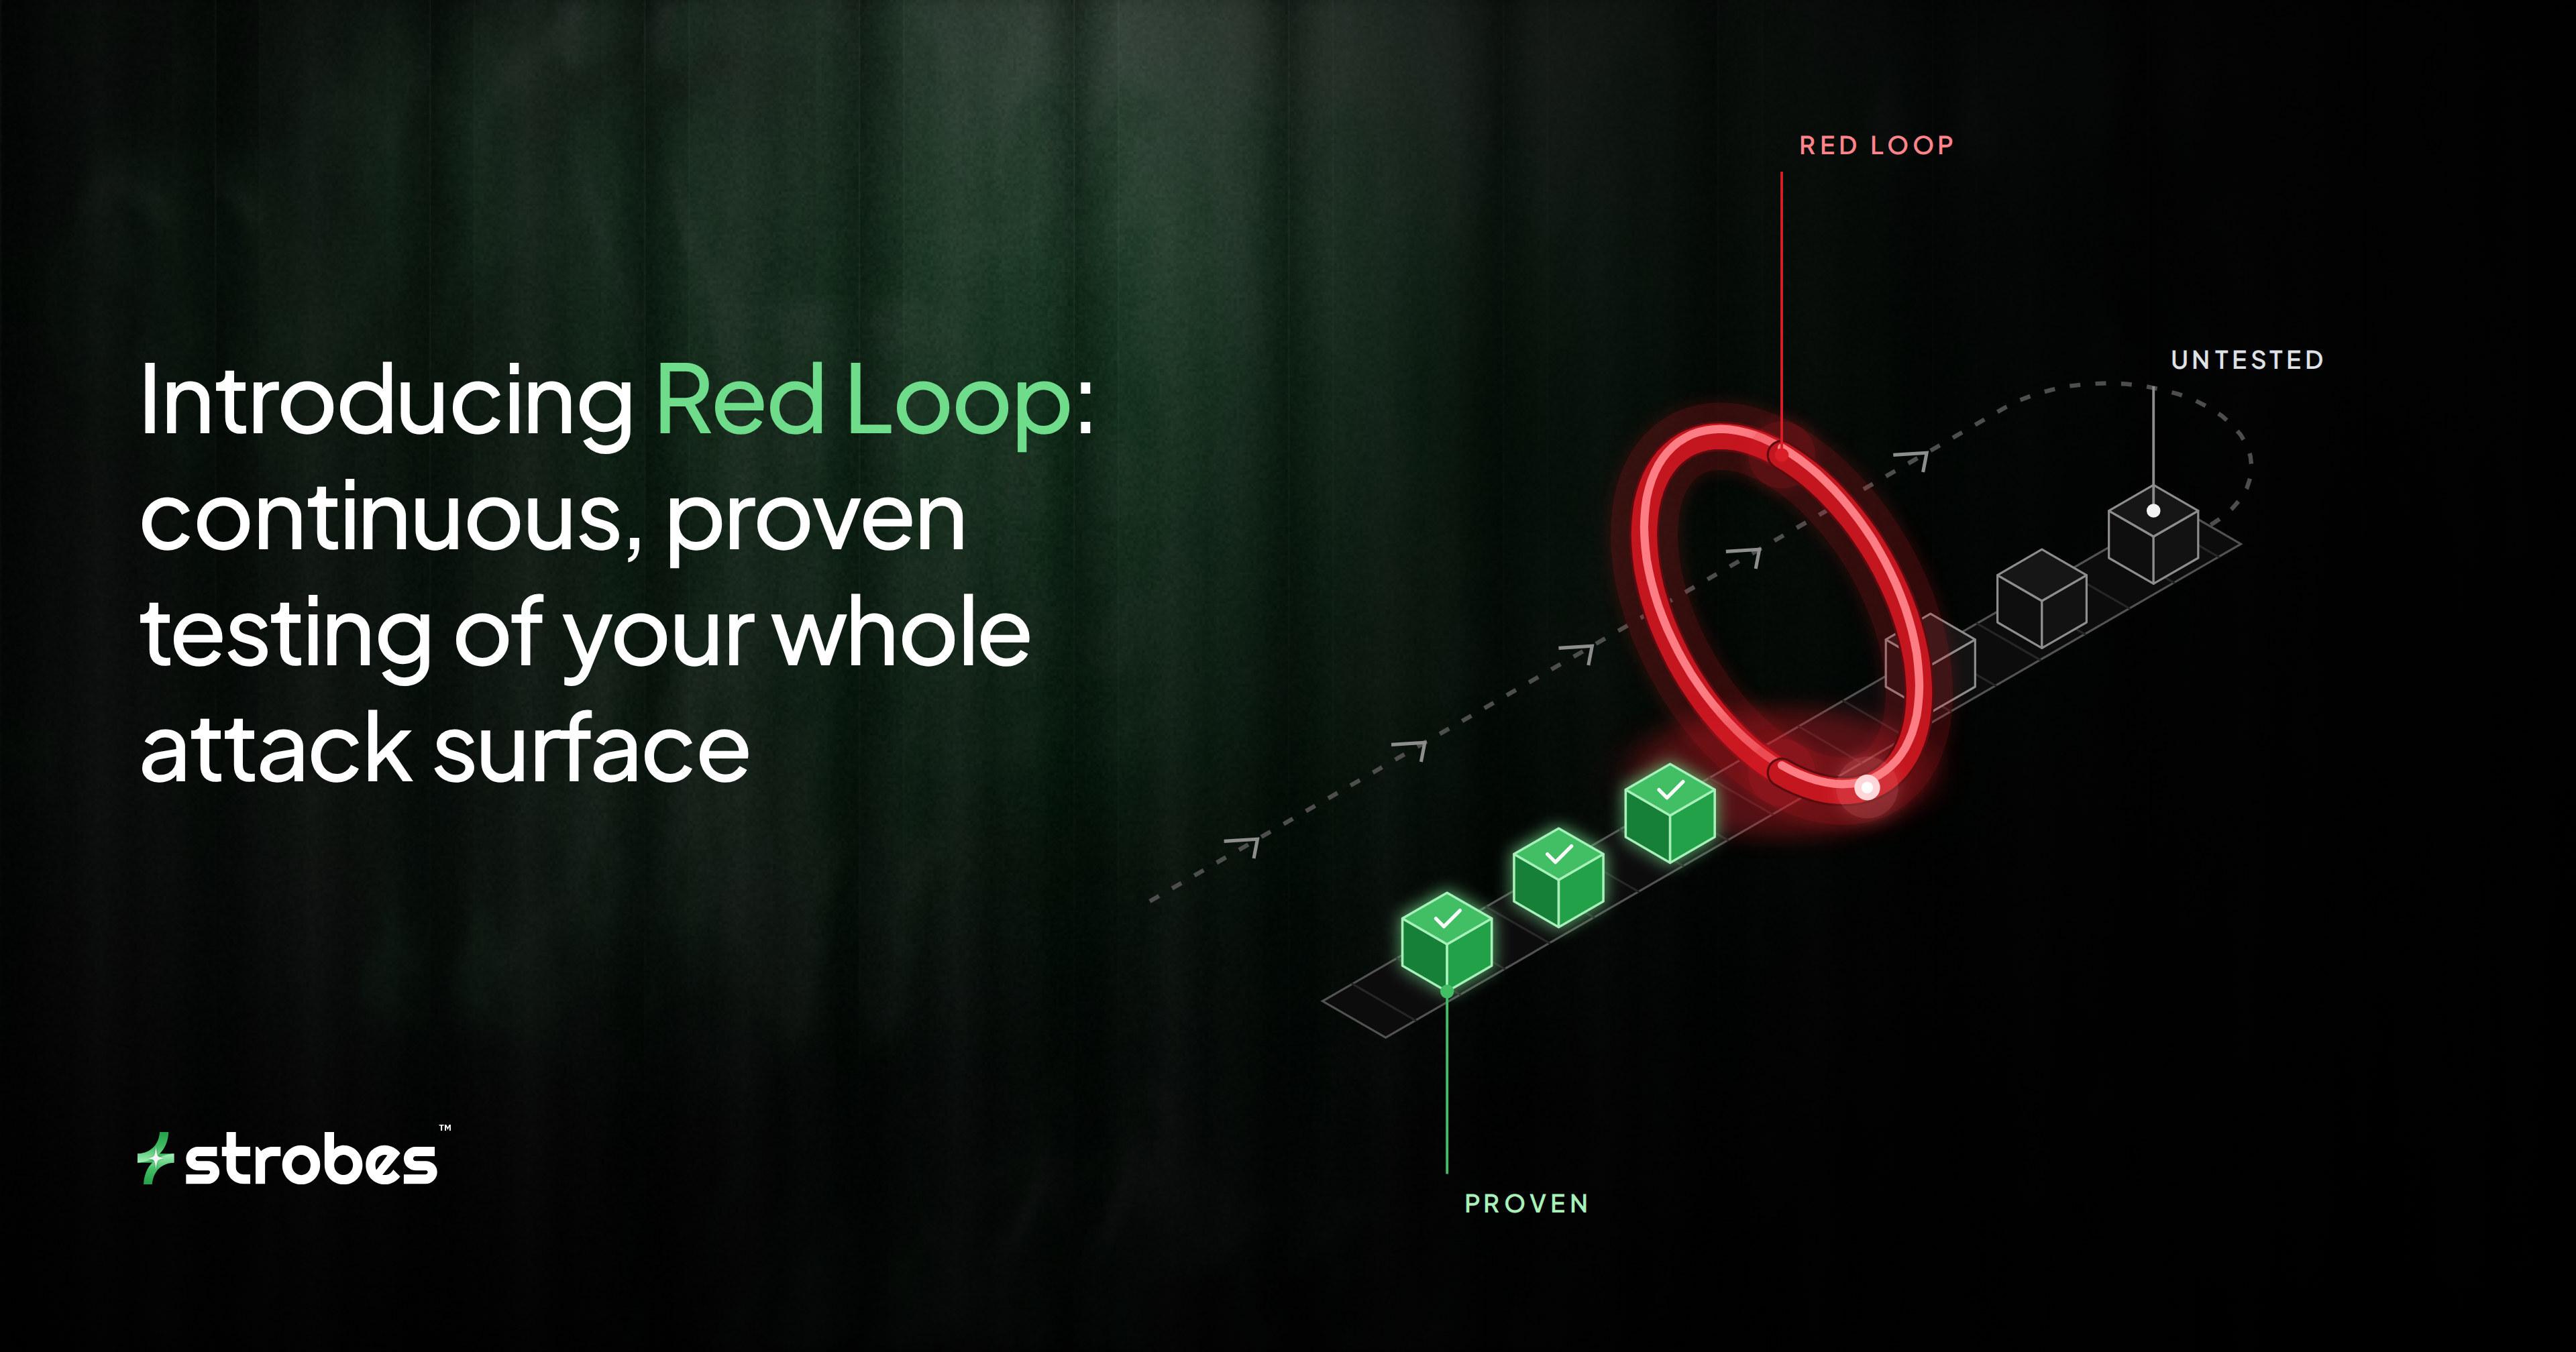
Introducing Red Loop: continuous, proven testing of your whole attack surface
Red Loop brings continuous offensive testing to Strobes Attack Surface Management. It discovers what you own, scans it the same way every time, and sends results to AI agents that attack and validate them. Only proven findings reach your queue.
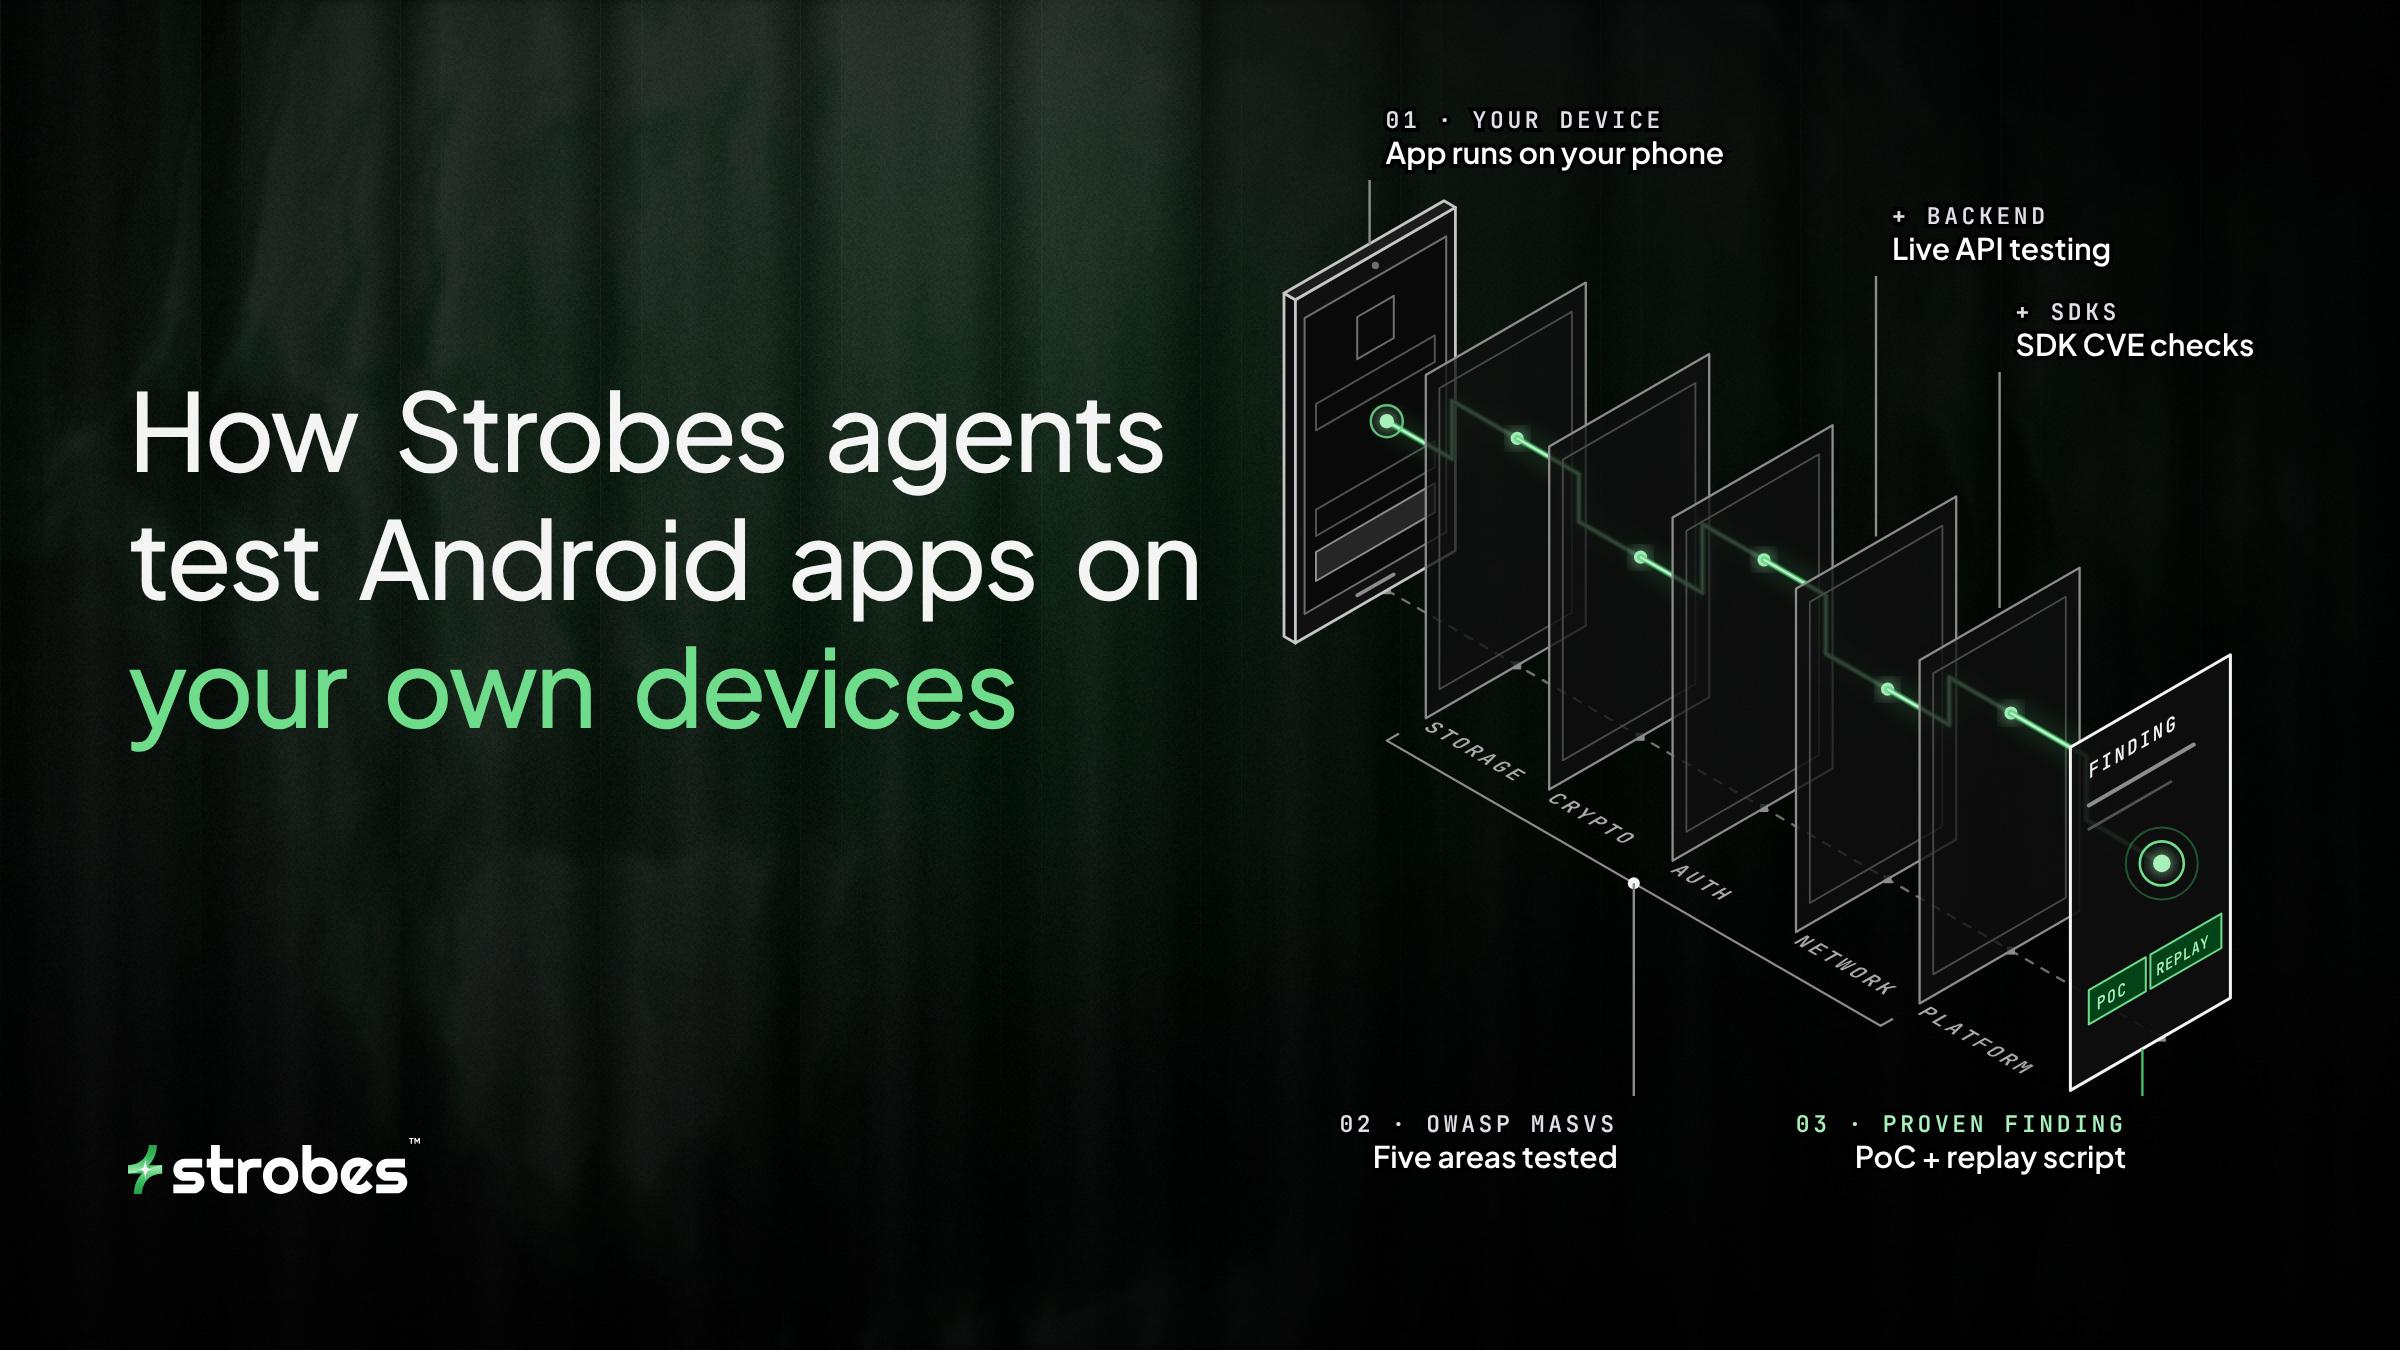
Strobes Agentic Pentesting Now Tests Android Apps on Your Own Devices
Strobes Agentic Pentesting now runs Android app pentesting on your own phones and emulators: live crawling, traffic interception, Frida instrumentation, and verified findings.
Strobes joins OpenAI's Daybreak program
OpenAI gates its cyber models behind an application, identity checks, and workspace scoping. Strobes is now verified for Daybreak.
Three months inside Anthropic's Cyber Verification Program at Strobes
Strobes has run Claude-powered agentic pentests under Anthropic's Cyber Verification Program since June 2026. Here's what the program gates and what changed in three months.
How Strobes AI identifies and exploits a SQL injection vulnerability
See how Strobes AI runs autonomous SQL injection testing, finding an injectable parameter, proving exploitability, and shipping evidence for remediation.
Strobes Agentic Pentesting: A pen-tester experience and point of view
Eleven validated Critical and High findings from Strobes AI's autonomous pentesting agents, each with the agent's reasoning, the request sent, and the response that proved it.
Gartner SRM 2026 Broke Something I Believed About Enterprise Security
Strobes CEO Venu Rao shares his takeaways from Gartner Security & Risk Management Summit 2026: everyone can find vulnerabilities, almost no one has cracked fixing them.
Is Claude Mythos the End of Pentesting?
Claude Mythos found thousands of zero-days in Linux, browsers, and Apache. Does that make pentesting platforms obsolete? Understanding why models, harnesses, and platforms are three different things -- and why smarter AI makes Strobes more valuable, not less.
Strobes VI Now Tracks Supply Chain Attacks, Ransomware Groups, and Threat Actors
224,487 supply chain incidents. 1,251 threat actors. Ransomware groups tracked in real time. Strobes VI now provides the threat intelligence layer that powers proactive exposure management, starting with the lessons from the Axios npm compromise.
How Strobes AI Turns a Supply Chain Zero-Day into a Full Exposure Assessment in Under 30 Minutes
When the axios npm package was compromised on March 31, 2026, Strobes AI agents autonomously performed incident response, identified every exposed repository across the attack surface, and generated a complete exposure assessment with remediation tasks in under 30 minutes.
How to Write an Effective AI Agent Skill: The Four-Layer Architecture
Most teams building AI agents get the ratio wrong: 90% code, 10% methodology. Here is the four-layer architecture Strobes uses to build skills that run complete security assessments autonomously.
Strobes AI: The Agent Stack Specialized for Offensive Security
A deep-dive into the multi-agent architecture behind Strobes AI — 12 purpose-built offensive security agents, the Skills system, Human in the Loop governance, and the architectural properties that make continuous exposure management viable at scale.